Cybercrime Law Dissertation Topics on Hacking, Ransomware and Digital Evidence
Questions to settle before you pick a cybercrime law topic
These cybercrime law dissertation topics are written for students who have already chosen law and now need a title a supervisor can approve. Each topic names the statute, case, treaty or dataset it rests on, so most of the narrowing is done before you start. All of them are free to use, adapt and combine.
- Do I want to argue about what the Computer Misuse Act 1990 should criminalise, or about how investigators and courts handle evidence once a cyber offence is suspected?
- Can I finish a doctrinal project on a Bill that Parliament has not yet passed, and how do I label it honestly?
- Which authority do I need first: a section of an Act, a Court of Appeal judgment, a regulator’s decision or a treaty text?
- Do I need technical knowledge of ransomware, encryption or blockchains, or can judgments and official reports carry the technical detail?
- Is my question about England and Wales, or will I compare it with a treaty or another country’s law?
- Will my project need ethics approval, or can public legal sources answer it?
The list leans towards criminal law and criminal procedure: offences, investigation powers, evidence, and the regulators and treaties that support enforcement. Data protection, intellectual property and contract questions about technology sit in the wider cyber law dissertation topics, while offences that have nothing to do with technology sit in the criminal law research areas.
Position correct as of October 2026. Several items move quickly: the Cyber Security and Resilience Bill was still in the House of Lords, reform of the Computer Misuse Act had been announced for a National Security Bill, the UN Convention against Cybercrime was waiting for ratifications, and the Crime and Policing Act 2026 was commencing in stages. Check Parliament’s Bills service and legislation.gov.uk for the current status before you submit. Also check your own university’s rules on ethics, referencing and word limits, because they differ between institutions and countries.
Computer Misuse Act 1990 dissertation topics: hacking, denial of service and reform
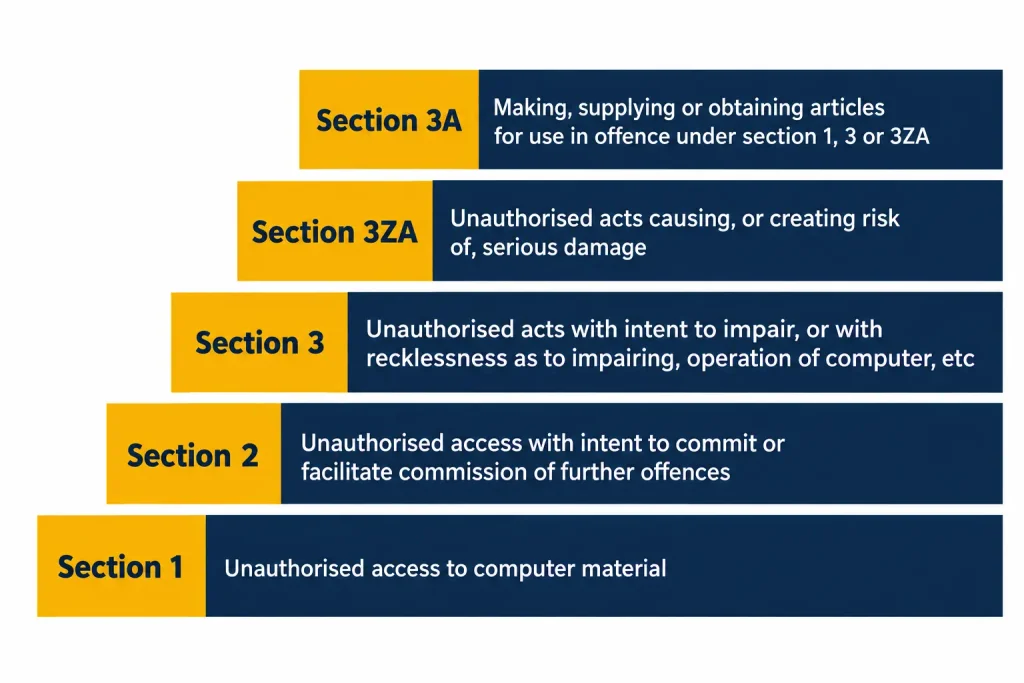
The Computer Misuse Act 1990 has five core offences: unauthorised access (section 1), access with intent to commit further offences (section 2), unauthorised acts with intent to impair (section 3), unauthorised acts causing serious damage (section 3ZA, added by the Serious Crime Act 2015) and making or supplying articles for use in offences (section 3A). Because the Act is old and reform has been announced, nearly every question below has a live reform angle. Students with a technical streak can pair these with the technical side of cybersecurity.
1. How should a statutory defence to section 1 of the Computer Misuse Act 1990 define the researcher it protects: by accreditation, by prior authorisation or by public interest?
In Lords Grand Committee on 7 September 2026 a Home Office minister said the Government proposes a defence to section 1 for accredited cyber security researchers, and the May 2026 King’s Speech placed Computer Misuse Act reform in the National Security Bill. Treat the defence as a proposal, not law. A strong project would compare accreditation with the safe harbours that peers were told exist in Portugal, France and Australia, test each model against scanning and vulnerability disclosure scenarios, and set out the safeguards a defence would need. It suits an LLM or a confident LLB doctrinal project, and Hansard plus the CyberUp Campaign proposals are the main sources.
2. Where does “access of the kind in question” in section 17(5) of the Computer Misuse Act 1990 draw the line for insiders who misuse authorised credentials, after R v Bignell [1998] and R v Bow Street Magistrates, ex p Allison [2000] 2 AC 216?
These two decisions are the starting authorities on whether someone with some authority can still commit section 1 by looking at data for an improper purpose. Read the judgments closely, then test the reasoning against modern role-based permissions in cloud systems. A good aim is a reform proposal on how “authorisation” should be drafted. An LLB student can keep to the two cases and one modern scenario.
3. Where does implied consent to receive email or web traffic end for the purposes of section 3 of the Computer Misuse Act 1990, as tested in DPP v Lennon [2006] EWHC 1201 (Admin)?
In Lennon the Divisional Court held that implied consent to receive email is not unlimited, comparing it to a letter-box that accepts letters but not a flood of rubbish. Parliament then amended section 3 through the Police and Justice Act 2006 and raised the maximum sentence to ten years. Examine how the same reasoning applies to distributed denial-of-service attacks run through botnets, where no single request looks unlawful. The core case is short, so the topic works at undergraduate level, and you can read the judgment free on the National Archives’ Find Case Law service.
4. Is section 3ZA of the Computer Misuse Act 1990 (serious damage, life maximum) the right charge for attacks on transport and health services, and how should “significant risk” be proved?
Section 3ZA covers unauthorised acts that create a significant risk of serious damage to human welfare or national security. In September 2025 two defendants were charged with conspiring to commit such acts against Transport for London, and both entered not guilty pleas. Check the current stage of that prosecution before citing it, and treat allegations as allegations. Build your analysis on the statutory test instead, comparing the listed heads of damage, such as disruption to transport or health services, with purely economic loss caused by the same attack. It suits an LLM or a strong LLB.
5. Is the “likely to be used” limb of section 3A of the Computer Misuse Act 1990 a workable line for dual-use security tools, or should liability require intent?
Section 3A criminalises making, supplying or obtaining articles for use in offences, including where a person believes the article is likely to be used that way. Penetration testing frameworks, password crackers and port scanners all have lawful uses, so the “likely” limb matters. A project could review prosecutions, Crown Prosecution Service guidance and industry practice, then propose clearer statutory factors for suppliers. It suits students who like drafting and do not want to run interviews.
6. How should Cyber Crime Risk Orders be designed so that they restrain cyber offenders without becoming preventive orders by another name?
The May 2026 King’s Speech announced Cyber Crime Risk Orders as part of the National Security Bill, alongside new powers to search people believed to be concealing evidence for suspects. Detailed wording was not available in the sources checked, so frame the project around design questions: threshold, standard of proof, duration and review. Compare Serious Crime Prevention Orders under Part 1 of the Serious Crime Act 2007 and the guidance in R v Hancox and Duffy [2010] EWCA Crim 102. Label the reform status clearly throughout.
7. When does automated scanning for exposed systems amount to causing a computer to perform a function with intent to secure access under section 1 of the Computer Misuse Act 1990?
Security researchers scan the internet for known vulnerabilities, and campaigners quoted in the trade press describe the Government’s planned protection as focused on this kind of activity. The legal question is whether a probe that returns a banner or confirms a flaw is an attempt to secure access, and whether the person has the knowledge section 1 requires. Apply the section 1 elements to three concrete scanning scenarios, then say what a defence would change. It suits an LLB or LLM student.
8. What counts as a “significant link with domestic jurisdiction” under sections 4 and 5 of the Computer Misuse Act 1990 when attacker, botnet and victim sit in different countries?
Sections 4 and 5 give English courts jurisdiction where at least one significant link exists, such as the accused or the target computer being in England and Wales. The “substantial measure” approach in R v Smith (Wallace Duncan) (No 4) [2004] EWCA Crim 631 offers a useful comparison for other offences. Use hypothetical botnet scenarios and ask how a prosecutor could assert jurisdiction in each. Add the Budapest Convention if you want comparative depth.
9. Section 170 of the Data Protection Act 2018 or section 1 of the Computer Misuse Act 1990: which offence better fits an employee who browses records they are allowed to open?
Insider snooping often involves access the system permits, which strains section 1 but may satisfy the unlawful obtaining offence in section 170. Use prosecution guidance and enforcement notes from the Information Commissioner’s Office to test which charge prosecutors choose and why. Plain language and short sources make this topic workable at undergraduate level.
10. Is there a case for a dedicated Sentencing Council guideline for Computer Misuse Act offences, based on a review of Court of Appeal sentencing authorities?
Check the Sentencing Council’s current list of guidelines first, because the answer depends on what exists today. If none covers these offences, collect Court of Appeal decisions on sections 1, 3 and 3ZA, map the factors judges weigh, and argue what a guideline should say about harm and culpability. It is a good choice if you like data and short judgments.
11. How should the Code for Crown Prosecutors and the Sentencing Council’s guideline on children and young people apply to hackers who offend as teenagers and are sentenced as adults?
Some well-publicised cyber prosecutions involve defendants who were under 18 when the alleged offending began. Examine diversion routes such as the National Crime Agency’s Cyber Choices programme, the public interest test and sentencing principles for young offenders. A criminology angle can sit beside the doctrinal analysis, and the criminology dissertation topics offer method ideas.
12. What does R v Gold and Schifreen [1988] AC 1063 show about why the Computer Misuse Act 1990 was needed, and what should that history teach reformers now?
Gold and Schifreen accessed a messaging service without permission, but the courts quashed their forgery convictions, which pushed Parliament towards a specific hacking offence. The story gives an undergraduate a clear legal-history chapter and a way to ask whether ageing legislation should be rewritten or patched. Only a handful of sources are needed.
13. Can a bug bounty programme’s terms operate as authorisation under section 17(5) of the Computer Misuse Act 1990 when the tested system is hosted by a third-party cloud provider?
Authorisation depends on who is entitled to control access. If a vendor invites testing but the infrastructure belongs to a cloud host or a customer, the invitation may not cover everything the researcher touches. Draft a model scope clause, test it against section 17, and compare any published safe-harbour language. Contract law knowledge helps, but the question remains a criminal one.
Ransomware and extortion law dissertation topics
Ransomware reaches criminal law through several doors at once: the Computer Misuse Act, blackmail, money laundering and sanctions. Policy is also moving, because the Home Office consulted on a payment ban and reporting regime in 2025.
14. Should an offence of paying a ransom, as proposed for public bodies and operators of critical national infrastructure, include a necessity or duress defence for hospitals and schools?
The Home Office consulted from 14 January to 8 April 2025 on a targeted payment ban, a payment prevention regime and mandatory reporting, and the Government later said it would proceed after about 72 per cent of respondents backed a ban for public sector bodies and critical infrastructure. Commentary on the May 2026 King’s Speech noted that it did not mention the proposals, so the legislative route is unclear. Frame your project around the enduring design question: who is covered, what defences exist and how a ban interacts with insurance. Check the current status before you write.
15. Does paying a ransom to a person on the UK cyber sanctions list already breach the Cyber (Sanctions) (EU Exit) Regulations 2020, and what strict liability exposure follows for victims and negotiators?
Financial sanctions breaches can attract civil penalties enforced by the Office of Financial Sanctions Implementation without proof of fault, while criminal offences generally require knowledge or reasonable cause to suspect. Map the offence and penalty provisions, then test them against a negotiation in which the group’s identity is uncertain. A comparative note on US Treasury advisories on ransomware payments adds depth.
16. Would a mandatory ransomware reporting duty engage legal professional privilege or the privilege against self-incrimination, and how do Australia’s limited-use rules answer the problem?
Australia’s Cyber Security Act 2024 restricts how information in ransomware payment reports can be used, including making it inadmissible in civil penalty proceedings under that Act. Compare that approach with existing UK duties in the Network and Information Systems Regulations 2018 and with the reporting proposals. The project is doctrinal and comparative, so no interviews are needed.
17. How well has the 72-hour ransomware payment reporting duty in Part 3 of Australia’s Cyber Security Act 2024 worked since it commenced on 30 May 2025?
The duty applies to businesses with turnover above A$3 million and to critical infrastructure entities, with civil penalties of up to 60 penalty units for failing to report and an education-first phase that ran until 31 December 2025. Evaluate it against its stated aims using regulator statistics and annual reports from the Australian Signals Directorate, then ask what the UK could copy. Students outside Australia can still use the legislation and public reports, since the design is the point.
18. Does insurance reimbursement of ransoms undermine deterrence, and could insurers or negotiators face money laundering liability under sections 327 to 329 of the Proceeds of Crime Act 2002?
Section 328 criminalises entering into arrangements that facilitate the retention or control of criminal property, and an authorised disclosure route can protect those who report. Analyse whether paying clean funds to a criminal creates liability for the payer’s side at all, and how the consent regime works in practice. The topic suits LLM students interested in financial crime.
19. Is blackmail under section 21 of the Theft Act 1968 or section 3ZA of the Computer Misuse Act 1990 the better charge for groups that threaten to publish stolen data without encrypting any systems?
Data-theft extortion has grown alongside encryption-based ransomware. Compare the elements of blackmail, which centre on an unwarranted demand with menaces, with the Computer Misuse Act offences and the sentences each offers. This analysis applies to England and Wales; Scottish students should substitute the common law crime of extortion.
20. How does the free, deliberate and informed act principle in R v Kennedy (No 2) [2007] UKHL 38 apply to causing a death through a ransomware attack on a hospital supplier?
Official statements have linked an attack on NHS services to a patient’s death, which raises questions of causation, gross negligence and whether a section 3ZA charge adds anything. Study the causation test in Kennedy, then ask whether a death after delayed care is a foreseeable consequence of the attacker’s act. No primary research is needed, but treat any specific incident as alleged unless a court or coroner has made findings. It suits an LLM.
Cyber-enabled fraud and scam law dissertation topics
The Fraud Strategy 2026 to 2029 describes fraud as the largest crime type in the UK, so a fraud project rarely lacks material. These topics also connect to the banking law topics if you want the payments side in more depth.
21. Can a person “make” a false representation under section 2 of the Fraud Act 2006 through an AI system that generates and sends the message without human review?
Section 2(5) already contemplates representations submitted to a system or device “with or without human intervention”, but the harder question is who makes the representation and who has the required knowledge. The Law Commission’s July 2025 discussion paper gives an example of a company whose AI sends false statements that no employee checked, and shows how mental-element rules strain. Ground your argument in dishonesty under Ivey v Genting Casinos [2017] UKSC 67 as well as the statutory elements.
22. Do sections 6 to 8 of the Fraud Act 2006 give prosecutors enough to reach phishing-kit developers who never contact a victim?
Section 6 covers possessing articles for use in fraud, section 7 covers making or supplying them, and section 8 defines “article” to include data held electronically. Examine the intent requirements, then compare section 3A of the Computer Misuse Act. Look for convictions in CPS and press sources and note how few there are.
23. Is the Payment Systems Regulator’s 50:50 reimbursement rule, with its £85,000 cap in force since 7 October 2024, a better deterrent than criminal enforcement against mule account holders?
Sending and receiving firms share reimbursement of authorised push payment scams over Faster Payments and CHAPS, and an independent evaluation published on 1 July 2026 reported roughly a 21 per cent fall in in-scope losses in the first year. Combine the regulator’s published data with a doctrinal analysis of why the criminal law reaches few mules. The design mixes doctrinal work with secondary data, and it needs no participants.
24. Does the “adequate consideration” exception in section 329(3)(c) of the Proceeds of Crime Act 2002 protect young people who allow their accounts to be used as money mules?
The question is practical for any student who has been offered easy money to “receive and forward” payments. Examine how prosecutors weigh knowledge or suspicion, the authorised-disclosure regime and sentencing practice. Plain-language sources include banking-sector warnings and CPS guidance.
25. Where does “associated person” in section 199 of the Economic Crime and Corporate Transparency Act 2023 end when fraud runs through outsourced call centres, platforms and cloud suppliers?
The failure to prevent fraud offence came into force on 1 September 2025 for large organisations, and it depends on an associated person committing a listed fraud offence to benefit the organisation. The Home Office guidance published on 6 November 2024 sets six principles for reasonable procedures, and the CPS and Serious Fraud Office updated their corporate prosecutions guidance in August 2025. Apply the definition to a supply chain scenario and ask whether cyber-enabled impersonation by outsiders can ever be caught. The topic links naturally to company law ideas.
26. How far can the fraudulent advertising duty in the Online Safety Act 2023 be enforced before Ofcom has completed its register of categorised services?
The duty applies to the largest services, so the register of Category 1 and 2A providers matters. Ofcom’s roadmap shows the next steps, and the Fraud Strategy 2026 to 2029 treats online fraud as a key enforcement focus. Check the roadmap on the day you finalise your title, since milestones shift.
27. What does the Fraud Strategy 2026 to 2029 change for victims who want a prosecution, given its £250 million budget, planned Online Crime Centre and Report Fraud service?
Published on 9 March 2026, the strategy rests on three pillars (disrupt, safeguard and respond) and promises a Fraud Victims Charter by mid-2027. Compare its promises with outcomes in police data and Crime Survey estimates for fraud. It makes a realistic evaluation project for a law student with a criminology interest.
28. Could the civil penalties for fraud that the Fraud Strategy 2026 to 2029 says the Government will consider sit alongside the Fraud Act 2006 without weakening due process?
The strategy says additional civil penalties will be considered, so label them as a proposal. Compare civil penalty regimes in financial regulation, the burden and standard of proof, and the “criminal charge” analysis under Article 6 ECHR drawn from Engel v Netherlands (1976). The topic suits an LLM with an interest in regulatory enforcement.
29. Does mandatory identity verification of company directors reduce shell-company fraud, and how could Companies House data test the claim?
The Fraud Strategy commits to mandatory identity verification for all directors by the end of 2026, building on the Economic Crime and Corporate Transparency Act 2023. A dataset project could compare dissolution and fraud-flag patterns before and after verification, using the register’s free data. You will need basic statistics, and the statistical test selector can help you choose a test.
30. How well does the Sentencing Council’s definitive guideline on fraud, bribery and money laundering offences capture the harm of high-volume, low-value online fraud?
The guideline uses loss and intended loss as key harm measures, which can hide the cumulative effect of many small victims. Collect recent Court of Appeal and Crown Court sentencing remarks and test whether the harm categories track real-world impact. Check the current version of the guideline before you begin.
31. Should telecoms providers carry regulatory or criminal liability for SIM-farm and number-spoofing fraud, and how would Ofcom’s planned consultation interact with the Fraud Strategy 2026 to 2029?
The strategy refers to a consultation with Ofcom later in 2026 on extending rules about phone numbers and SIM-based fraud beyond the largest operators. Treat the consultation as pending and focus on design: duties, thresholds and enforcement. Compare the Online Safety Act model for platforms.
32. Can people coerced into running online scams in overseas “scam compounds” rely on the statutory defence in section 45 of the Modern Slavery Act 2015 if they are charged in the UK?
United Nations human rights reports have described trafficked workers forced to commit online fraud. Section 45 offers a defence for victims compelled to commit certain offences, but it excludes listed offences and requires a link to exploitation. Study the schedule of excluded offences, appellate treatment of the defence and CPS public interest guidance on potential victims of trafficking. This is a sensitive subject, so use published reports and judgments rather than interviews with victims.
Cryptoasset crime and digital asset law dissertation topics
The Property (Digital Assets etc) Act 2025 received Royal Assent on 2 December 2025. It confirms that a thing is not prevented from being the object of personal property rights merely because it falls outside the two traditional categories. For finance and market material, the cryptocurrency research ideas sit alongside these legal questions.
33. Do cryptoassets recognised under the Property (Digital Assets etc) Act 2025 now fit “property” under section 4 of the Theft Act 1968, and should wallet hacks be charged as theft or under the Computer Misuse Act?
Section 4 defines property widely, including intangible property, and the 2025 Act leaves courts to develop the “third category” of personal property. Examine whether “belonging to another” and “appropriation” work for private keys and on-chain transfers. Compare charging practice in published cases and note gaps. The doctrinal depth suits an LLM.
34. How have English courts used AA v Persons Unknown [2019] EWHC 3556 (Comm) and later proprietary injunctions to freeze stolen cryptoassets, and does the 2025 Act change the analysis?
AA v Persons Unknown treated bitcoin as property in a ransomware setting, and its reasoning predates the Act. Analyse later decisions, service on anonymous defendants and the use of Bankers Trust orders against exchanges. The remedies are civil, but they shape what victims of cybercrime can actually recover.
35. What does the High Court’s handling of Zhimin Qian’s 61,000 bitcoin reveal about restitution to victims compared with state retention under the Proceeds of Crime Act 2002, including section 281 claims?
Qian was sentenced to 11 years and 8 months at Southwark Crown Court in November 2025 for possessing and transferring criminal property, and the Crown Prosecution Service began civil recovery proceedings in the High Court. Victims in China have made section 281 claims, and a preliminary issue about which country’s law governs those claims was before the court in 2026. Because the proceedings were continuing, check the latest judgment before you rely on any ruling and avoid predicting the result. It makes a strong case study in virtual asset recovery.
36. Do the cryptoasset seizure, detention and civil recovery powers added to the Proceeds of Crime Act 2002 by the Economic Crime and Corporate Transparency Act 2023 reach assets in non-custodial wallets?
The powers work best where an exchange can freeze assets, whereas self-hosted wallets depend on the owner’s keys. Review the statutory definitions, the practical seizure of recovery phrases and any decisions applying the powers. The topic suits LLM level.
37. Is operating a non-custodial mixing protocol a money laundering offence under sections 327 to 329 of the Proceeds of Crime Act 2002, and what does the US litigation over Tornado Cash suggest about the limits of sanctions and criminal law?
Mixing software serves privacy-seeking users and launderers alike. Examine the knowledge and suspicion requirements for developers who do not control funds, then compare the US sanctions and prosecution litigation. Treat ongoing proceedings with caution and cite final judgments only.
38. Do the UK’s “travel rule” obligations for cryptoasset businesses, in force since 1 September 2023, improve tracing of cross-border transfers, and how could success be measured?
The rule requires information to accompany transfers, but unhosted wallets and offshore exchanges limit its reach. Design a measurable test using regulator reporting, suspicious activity report statistics and industry research. The topic suits a project that blends law with modest data analysis.
39. Can exploiting a smart-contract flaw without breaking into any system be dishonest under section 2 or 3 of the Fraud Act 2006, applying Ivey v Genting Casinos [2017] UKSC 67 and R v Barton and Booth [2020] EWCA Crim 575?
Some decentralised finance “exploits” use code exactly as written. The legal issue is whether a false representation or a failure to disclose exists, and whether the conduct is dishonest by the standards of ordinary decent people. Use published reports and court filings to build two or three scenarios, but analyse them under English law.
40. How will the planned FCA authorisation regime for cryptoasset firms interact with the criminal offences for unregistered cryptoasset business under the Money Laundering Regulations 2017?
Commentary on the Fraud Strategy describes cryptoasset authorisation rules planned from 2027. Compare criminal offences for unregistered activity with Financial Conduct Authority enforcement, and examine how a new authorisation gateway changes risk for small operators. This is a pending regime, so confirm commencement dates before you finalise the title.
Online Safety Act 2023 and image-based abuse dissertation topics
Part 10 of the Online Safety Act 2023 created communications offences that came into force on 31 January 2024, and later legislation added deepfake and takedown rules. The media law topics cover the free expression side in more depth. The CPS guidance on communications offences is a free starting point for the first few topics.
41. Is the “non-trivial psychological or physical harm” threshold in section 179 of the Online Safety Act 2023 pitched correctly, compared with the repealed section 127(2) of the Communications Act 2003?
Section 179 replaced older false-message offences and requires knowledge of falsity and intent to cause non-trivial harm, which commentators say raises the bar for prosecution. Compare charging data and decisions under both regimes, and weigh freedom of expression under Article 10 ECHR.
42. Does section 181 of the Online Safety Act 2023 (threatening communications, up to five years) reach sustained pile-ons where no single message is a threat?
The offence targets individual threats, so collective abuse raises attribution and course-of-conduct questions. Compare the Protection from Harassment Act 1997 and the Law Commission’s 2021 report Modernising Communications Offences. The analysis is doctrinal, with optional case-law mapping.
43. How should courts read “encouraging or assisting serious self-harm” in section 184 of the Online Safety Act 2023 where messages come from peer-support communities?
The offence turns on intent to encourage or assist serious self-harm, and on what counts as serious, which matters for online recovery spaces. Keep to the legal elements and published decisions. This is a sensitive area, so avoid describing methods and treat the analysis as a question of drafting and intent.
44. Is the fault element in section 66A of the Sexual Offences Act 2003 (cyberflashing, inserted by section 187 of the Online Safety Act 2023) too hard to prove at scale?
The offence requires intent that the recipient will see the image and either intent to cause alarm, distress or humiliation, or a sexual gratification purpose combined with recklessness about alarm or distress. Compare it with the Law Commission’s 2022 recommendations on intimate image abuse and with prosecution data when available. A short statutory text makes it manageable for undergraduates.
45. Are the creation and request offences in sections 66E and 66F of the Sexual Offences Act 2003, in force since 6 February 2026, a proportionate response to deepfake intimate images made for private use?
Section 138 of the Data (Use and Access) Act 2025 inserted these offences, so an image can be unlawful even if it is never shared, and a request counts even if no image is created. The commencement regulations confirm the 6 February 2026 start. Examine fault elements, the reasonable belief in consent, and sentencing, then ask whether criminalising creation adds protection beyond the sharing offences.
46. How should “purported intimate image generator” be defined in the Crime and Policing Act 2026 so that the offence reaches nudification tools but not general-purpose image models?
The Act creates offences of making or supplying generators of purported intimate images, and commentary notes that its wording differs from the parallel child sexual abuse image-generator offence. Some provisions commenced from 29 June 2026, so check which are in force. Compare the statutory language and draft a clearer definition. It suits students interested in AI law.
47. Is personal criminal liability for senior managers who fail to meet the 48-hour intimate image takedown duty in the Crime and Policing Act 2026 proportionate, compared with corporate officer liability under section 186 of the Online Safety Act 2023?
Commentary describes a 48-hour takedown duty with personal criminal liability for failures. Confirm commencement of each provision, then compare the structure of the offence with section 186. Draft evaluation criteria such as clarity, fairness and effect on small platforms.
48. What do Ofcom’s first Online Safety Act penalty decisions, such as the £950,000 fine announced in May 2026 against an online suicide forum, show about how “proportionate measures” are judged?
Ofcom found breaches of duties including illegal content risk assessment, preventing exposure to priority illegal content, swift takedown and complaints procedures. Compile Ofcom’s published decisions into a small dataset and code the factors it cites. The design is document analysis with no human participants.
49. Can the illegal content duties in section 10 of the Online Safety Act 2023 be applied to a messaging service with large public channels, as Ofcom’s April 2026 investigation into Telegram tests?
Ofcom opened the investigation on 21 April 2026 into whether the provider is failing its illegal content duties in respect of child sexual abuse material. Do not predict the outcome. Instead, examine how the Act’s definitions of user-to-user service and content communicated publicly apply to hybrid services.
50. Can a section 121 technology notice ever lawfully require scanning of end-to-end encrypted messages, given the accredited technology and minimum-accuracy steps Ofcom must complete first?
Section 121 lets Ofcom require accredited technology to identify terrorism or child sexual exploitation and abuse content, and the roadmap explains that standards and an accreditation process must exist before notices can be used. Analyse the necessity and proportionality tests and Article 8 ECHR. Then compare the Investigatory Powers Act technical capability notices covered in the investigatory powers section below.
51. Why did Parliament create the flashing-images offence in section 183 of the Online Safety Act 2023, and did existing assault or communications law already cover it?
The offence responds to targeted attacks on people with photosensitive epilepsy and is sometimes called Zach’s Law. A short undergraduate project can trace the policy history, compare older offences and ask whether a specific offence was necessary. Only a few sources are needed.
52. Is the “course of conduct” requirement in the Protection from Harassment Act 1997 suited to stalking by spyware, location sharing and smart-home devices?
Technology-facilitated stalking can involve a single installation that watches a victim for months, which tests the idea of repeated acts. Review the stalking provisions in sections 2A and 4A, key authorities and CPS guidance. Combine this with the stalkerware question below if you want a wider project.
53. Does section 76 of the Serious Crime Act 2015 (controlling or coercive behaviour) capture spyware, location tracking and smart-home control, and how should courts treat digital evidence of coercion?
The Domestic Abuse Act 2021 extended the offence to abuse after separation. Examine how prosecutors prove serious effect and how app data, logs and device settings are used as evidence. Use published appeal decisions, which makes the topic suitable for criminology-minded law students.
54. Should supplying stalkerware be a standalone offence in England and Wales, or do existing laws on computer misuse, harassment and data protection already cover it?
Stalkerware is software marketed for covert monitoring, often of partners. Test section 3A of the Computer Misuse Act, section 170 of the Data Protection Act 2018 and the Protection from Harassment Act against typical vendor and user behaviour. Then draft a short reform proposal and consider consumer protection angles.
55. How should sextortion by threat to share intimate images be charged: as blackmail under section 21 of the Theft Act 1968 or as a threat offence under section 66B of the Sexual Offences Act 2003?
Section 66B, inserted by the Online Safety Act 2023, criminalises sharing and threatening to share intimate images, while blackmail requires a demand with menaces and a view to gain or loss. Compare sentencing, evidential burdens and victim support. Use official guidance and reported judgments, and avoid any material that depicts abuse.
56. Is the law applied to online incitement after the August 2024 disorder, including section 19 of the Public Order Act 1986, consistent with the communications offences in Part 10 of the Online Safety Act 2023?
Several people were prosecuted for online posts during and after the disorder, which raised questions about the line between stirring up hatred, threats and false communications. Compile published Court of Appeal and Crown Court sentencing decisions and compare the elements of each offence. Rely on judgments rather than press accounts when you describe individual cases.
57. Does the National Security Bill’s proposed offence of creating or sharing harmful violent material online draw a workable line with Article 10 ECHR?
The May 2026 King’s Speech said the National Security Bill would criminalise creating and sharing harmful violent material online. The text of the Bill is the first thing to check. Define the harm, compare existing offences for terrorist publications and the Online Safety Act duties, and test the proposal against Article 10.
Child safety online and cybercrime law dissertation topics
Cybercrime law and child protection meet in offences about images, grooming and facilitation. Use statutes, judgments and published statistics, never the underlying material. The wider child law dissertation topics cover family and welfare law.
58. How should a “child sexual abuse image-generator” be defined in the Crime and Policing Act 2026 so that fine-tuned models are caught without criminalising general-purpose model developers?
Commentary notes that before the Act, fine-tuned versions of off-the-shelf models optimised to produce abusive imagery were not illegal in themselves. Compare the statutory definition with the possession, making and supply offences for pseudo-photographs and prohibited images, and ask whether “optimised for” or “adapted for” is the better test.
59. What should “relevant internet activity” with intent to facilitate child sexual exploitation require under the Crime and Policing Act 2026 for moderators and administrators of sites hosting abuse material?
The Act criminalises carrying out relevant internet activity with the intention of facilitating child sexual exploitation and abuse, and commentary says it is aimed at roles such as moderators and administrators. Explore the mental element, protections for trust and safety staff, and how the offence works alongside Ofcom’s duties.
60. Is section 15A of the Sexual Offences Act 2003 (sexual communication with a child) well drafted for grooming that moves between gaming, social and encrypted messaging services?
Section 15A applies where an adult intentionally communicates with a child under 16 for sexual gratification. Study how prosecutors evidence communications across platforms and how encryption affects detection. Plain-language sources include CPS guidance and Ofcom’s illegal content codes.
61. How does the abuse of process doctrine in Attorney General’s Reference (No 3 of 2000) [2001] UKHL 53 (R v Looseley) apply to evidence collected by vigilante “paedophile hunter” groups and passed to police?
Looseley governs entrapment: state agents may not incite offences but may provide an opportunity. Private groups operate differently, which raises questions about admissibility under section 78 of the Police and Criminal Evidence Act 1984 and the role of police afterwards. Use reported cases and avoid describing any method of contacting minors.
62. What can Internet Watch Foundation annual data and the hash-matching measures in Ofcom’s Illegal Content Codes tell a researcher about how detection technology changes reporting patterns?
Ofcom has raised compliance concerns with file-sharing services that later adopted perceptual hash-matching technology. Use only published statistics and regulator updates, and never handle abusive material. A policy evaluation design suits LLM students with an interest in method.
AI-enabled crime and deepfake law dissertation topics
AI shifts the cybercrime question from “who clicked” to “who is responsible for what a system did”. The Law Commission’s discussion paper of July 2025 explores that gap. For the computing side, see the artificial intelligence dissertation topics.
63. Should the Law Commission’s “liability gap” for autonomous AI agents in criminal law be closed by new mental-element rules, a duty to supervise, or limited AI legal personality?
The discussion paper made no reform proposals, but it showed how criminal liability can fail when no person knew an AI system’s output was false, and it raised legal personality as an option for later debate. Compare the three models against a concrete scenario such as an AI customer-service or trading agent. It is a theory-leaning topic for an LLM or PhD.
64. When an AI agent exceeds its instructions and probes systems it was not told to touch, who commits the section 1 offence under the Computer Misuse Act 1990, and with what intent?
Agentic security tools can run reconnaissance at machine speed, a point industry commentators raised in the reform debate. Section 1 needs intent to secure access and knowledge that the access is unauthorised. Test those requirements against operator, developer and deployer roles, then draft a proposal for assigning responsibility.
65. Does English law need an offence of non-intimate deepfake impersonation, or do the Fraud Act 2006, defamation and harassment law already cover it?
Section 138 of the Data (Use and Access) Act 2025 covers intimate images, not synthetic voice or video used for scams, reputational harm or political deception. Map the gaps with three examples, then decide whether a new offence is justified. Comparison with other jurisdictions’ deepfake statutes would add depth.
66. Could section 106 of the Representation of the People Act 1983 (false statements about a candidate’s character) reach AI-generated audio or video about a candidate?
The section prohibits false statements of fact about a candidate’s personal character or conduct made to affect an election result. Examine “statement”, publication and the reasonable belief defence, then consider the role of the Electoral Commission and platform duties under the Online Safety Act.
67. Does the Online Safety Act 2023, as amended by the Crime and Policing Act 2026, bring general-purpose chatbots within the illegal content duties, or does that depend on later regulations?
The 2026 Act gives the Secretary of State power to make regulations on illegal AI-generated content and on AI services used to commit priority offences, and Ofcom has said AI-generated content is likely already in scope. Compare the statutory text with Ofcom’s statements and ask whether a regulation-making power is the right tool.
Investigatory powers, encryption and surveillance dissertation topics
Investigation powers give cybercrime law its sharpest human rights questions, and the human rights law topics offer wider Article 8 and Article 6 material. Several matters below are still running, so cite final decisions and treat live proceedings as unresolved.
68. How did R v A, B, D and C [2021] EWCA Crim 128 distinguish stored from transmitted data under section 4(4) of the Investigatory Powers Act 2016, and does that reasoning survive mass equipment interference?
The Court of Appeal held that EncroChat messages were admissible because they were intercepted while stored, and the equipment interference was authorised by a targeted equipment interference warrant. A later decision, [2023] EWCA Crim 282, summarises the key principles. Critique the stored or transmitted distinction and test it against newer technologies.
69. How far can a thematic targeted equipment interference warrant under section 99 of the Investigatory Powers Act 2016 lawfully reach, as examined in SF v NCA [2023] UKIPTrib 3?
The Investigatory Powers Tribunal considered the lawfulness of the warrant used to obtain EncroChat material. Read the reasoning and compare it with the Court of Appeal’s approach to admissibility. The topic suits students who want to study the Tribunal’s role.
70. Does section 253 of the Investigatory Powers Act 2016 allow the Home Secretary to require a provider to weaken end-to-end encrypted cloud storage, as the complaints by Apple, Privacy International and Liberty test?
Reporting in 2026 describes a second notice limited to UK users and a September 2026 hearing on the neither-confirm-nor-deny policy, with a full hearing reported as unlikely before 2027. Because proceedings continue, frame the analysis around the statutory power: what “technical capability” means, what limits necessity and proportionality impose, and how extraterritorial effect is handled. Privacy International’s case summary collects documents.
71. How should the neither-confirm-nor-deny policy for technical capability notices be tested against open justice, given the Tribunal’s 2025 refusal to hold Apple’s first hearing entirely in secret?
According to reports, the Tribunal said hearing everything in secret would be a fundamental interference with open justice, and it issued a short public judgment. Consider what open justice requires in security cases and compare closed material procedures in other courts.
72. Does compelled disclosure of passwords under sections 49 and 53 of the Regulation of Investigatory Powers Act 2000 remain compatible with the privilege against self-incrimination after R v S and A [2008] EWCA Crim 2177?
The Court of Appeal likened a password to the key of a locked drawer, an independent fact, and said the privilege would be engaged only if the data itself were incriminating. Test that reasoning for biometrics, passphrases held only in memory and the use of refusal as evidence, and compare Saunders v United Kingdom (1996). Recent prosecutions have included refusal charges, which you should treat as allegations unless a court has decided them.
73. Did Big Brother Watch v United Kingdom (Grand Chamber, 2021) and the Investigatory Powers (Amendment) Act 2024 cure the Article 8 weaknesses in bulk interception and bulk personal dataset regimes?
The Grand Chamber found violations in the old bulk interception regime and in certain acquisitions of communications data, and Parliament has legislated since. Evaluate the 2024 changes to bulk personal datasets against the Strasbourg criteria. It is a strong comparative option for human rights students.
74. Can a private company that “hacks back” to retrieve stolen data rely on any defence to section 1 of the Computer Misuse Act 1990, and what would an accredited-researcher defence change?
Active cyber defence by private firms is controversial. Examine whether necessity, self-defence or consent can apply and how law enforcement treats the practice. The proposed defence is limited to accredited researchers, so its effect on hack-back is a question for analysis rather than assumption.
75. What safeguards does Chapter 3 of Part 2 of the Police, Crime, Sentencing and Courts Act 2022 give victims and witnesses when police extract data from their phones, and how well do “voluntary” consent models work?
The Act gave a statutory basis for extracting information from devices with user agreement and requires a Code of Practice. Focus on privacy, necessity and proportionality, using the Code, regulator commentary and any published inspections. The topic is especially relevant to digital evidence in fraud and sexual offence trials.
Digital evidence and fair trial dissertation topics
Digital evidence is where cybercrime law meets criminal procedure. The Post Office Horizon scandal put the reliability of computer evidence on the political agenda, and the Post Office (Horizon System) Offences Act 2024 quashed affected convictions.
76. Should the common law presumption that computers operate correctly be replaced by a statutory reliability test for software-generated evidence?
The Ministry of Justice ran a call for evidence from January to April 2025 on the presumption, which dates from the repeal of section 69 of the Police and Criminal Evidence Act 1984 by the Youth Justice and Criminal Evidence Act 1999. Check whether the Government has published a response before you start. Then compare the position with civil proceedings, where no equivalent presumption applies.
77. How should the Crown Court test the authenticity of audio and video evidence when convincing synthetic media is cheap to produce, within section 78 of the Police and Criminal Evidence Act 1984 and the Criminal Procedure Rules?
Authentication is traditionally a matter of weight, but deepfakes may make admissibility rulings more demanding. Propose a pre-trial authentication protocol and compare it with approaches elsewhere, such as expert provenance evidence. It suits LLB students who like procedure and short statutory texts.
78. How should the “reasonable line of inquiry” test under the Criminal Procedure and Investigations Act 1996 and the Attorney General’s Guidelines on Disclosure apply to bulk phone extractions in cyber-enabled fraud trials?
A single phone can hold millions of messages, so disclosure duties meet practical limits. Examine the Guidelines, case management practice and the role of technology-assisted review. Check the current version of the Guidelines and any reforms announced since.
79. How did R v Atkinson [2021] EWCA Crim 1447 deal with hearsay and section 78 objections to EncroChat messages, and what lessons apply to other bulk-obtained message evidence?
After R v A, B, D and C settled the Investigatory Powers Act point, Atkinson addressed other admissibility objections. Compare it with later appeal decisions and identify which arguments remain open. The topic is a good case-law mapping project.
80. Are IP addresses, malware code similarity and device logs strong enough attribution evidence for the criminal standard in hacking trials, and what do appeal decisions say about expert evidence?
Attribution is often the weakest link in cyber prosecutions. Review the Criminal Practice Directions on expert evidence, reported appeals and Forensic Science Regulator guidance, and identify where juries need help. Some technical interest is useful, but no primary data are required.
81. How reliable are police-recorded cybercrime statistics compared with Crime Survey for England and Wales estimates, and what does the gap mean for reform arguments?
The Office for National Statistics reported an estimated 817,000 computer misuse incidents in the year ending June 2026, a 23 per cent rise on the previous year, while police-recorded data capture a different slice of offending. Compare the two series, note their limits, and discuss how reform debates use them. It is a measurement project that needs only light statistics.
Cross-border cybercrime enforcement, extradition and treaty dissertation topics
Cybercrime ignores borders, so enforcement depends on treaties, extradition and evidence-sharing rules. The EU law dissertation topics help with the Union instruments.
82. After Love v USA [2018] EWHC 172 (Admin), when does the forum bar in section 83A of the Extradition Act 2003 stop extradition of a UK-based hacker to the United States?
The Divisional Court’s judgment in Love was the first reported case in which the forum bar helped block an extradition, although commentators stress that the facts were extreme and that a separate ground based on Mr Love’s health also applied. Study the statutory factors and later decisions, and compare the alternative of prosecuting in the UK.
83. Does the Second Additional Protocol to the Budapest Convention (CETS 224) reduce the need for consent-based cross-border access under Article 32(b), given that it had only four ratifications by April 2026?
The Convention on Cybercrime has more than 80 parties, but the Second Additional Protocol on electronic evidence had been ratified by four states by April 2026, according to the Council of Europe. Compare its direct requests to providers and emergency mutual assistance with older routes. Check the Council of Europe treaty office for the current count.
84. Would joining the UN Convention against Cybercrime help or harm UK cooperation, given that it needs 40 ratifications and its human rights safeguards are contested?
The Convention was adopted in December 2024, opened for signature in Hanoi in October 2025 and remains open for signature in New York until 31 December 2026. The EU Council authorised the EU to conclude it in June 2026. Compare its conditions and safeguards article with Article 15 of the Budapest Convention, and check the UN Treaty Collection for the UK’s current status.
85. How will European Production Orders under Regulation (EU) 2023/1543, applicable from 18 August 2026, affect UK-based service providers that offer services in the Union?
The Regulation lets prosecutors in one Member State send binding orders directly to providers, with 10-day deadlines and 8 hours in emergencies, and providers must designate an establishment or legal representative in the EU. Denmark is not bound. Analyse extraterritorial reach, conflicts with UK law and the safeguards for fundamental rights.
86. Does the Crime (Overseas Production Orders) Act 2019, together with the UK-US Data Access Agreement, deliver faster access to overseas-held communications than mutual legal assistance?
The 2019 Act lets UK courts order overseas providers to produce electronic data where a designated international agreement exists, and the agreement with the United States is the leading example. Measure speed and refusal rates using any published government reporting, and compare them with letters of request. It suits a comparative procedural project.
Corporate liability and cyber regulation dissertation topics
Regulation does much of the work in preventing cybercrime, and the Cyber Security and Resilience Bill is the next major change. Questions here ask whether duties should be civil, regulatory or criminal.
87. Should the Cyber Security and Resilience Bill’s 24-hour and 72-hour incident reporting duties be backed by criminal offences, or kept as civil penalties?
The Bill, introduced on 12 November 2025, amends the Network and Information Systems Regulations 2018 to widen sectors, add managed service providers and set two-stage reporting. The House of Lords took Committee stage in September 2026, and Report stage was scheduled for 26 October 2026, so check the Bill’s current stage. Compare the penalty model with the EU’s NIS2 Directive.
88. Do directors’ duties under sections 172 and 174 of the Companies Act 2006 extend to oversight of cyber risk, applying the competence standard in Re Barings plc (No 5) [1999] 1 BCLC 433?
A board that ignores known cyber weaknesses faces questions about care, skill and diligence. The Cyber Security Breaches Survey 2025/26 reported that 43 per cent of businesses had a breach or attack in the past year, and the National Cyber Security Centre publishes governance guidance. Pair a company law framework with a short review of director disqualification decisions.
89. What “appropriate technical and organisational measures” under Article 32 of the UK GDPR did the ICO find Capita lacking in its £14 million penalty of October 2025, and how should liability be split between controller and processor?
The ICO fined Capita plc £8 million and Capita Pension Solutions £6 million after a 2023 attack exposed the data of about 6.6 million people, reducing a provisional £45 million figure after mitigation. Findings included a 58-hour response to a high-priority alert against a one-hour target. Use the monetary penalty notice as a primary source and compare other ICO cyber penalties.
90. After Lloyd v Google LLC [2021] UKSC 50, which procedural route lets large groups claim for a ransomware data breach, as in the group claim against Capita?
Lloyd limited opt-out representative claims for loss of control of data without proof of individual damage. Compare group litigation orders and representative actions, and use the Capita group claim as a case study. Keep to published pleadings and judgments.
91. Should managed service providers face regulatory penalties only, as the Cyber Security and Resilience Bill proposes, or criminal liability for negligent security failures that expose customers?
The Bill brings certain managed service providers within the NIS framework. Compare product safety and health and safety models of corporate offences, including the failure-to-prevent structure in section 199 of the Economic Crime and Corporate Transparency Act 2023.
92. Is the civil penalty regime under the Product Security and Telecommunications Infrastructure Act 2022, in force since 29 April 2024, a sufficient answer to insecure smart devices compared with criminal liability?
The regime bans default passwords and requires vulnerability reporting for connected consumer products. Compare enforcement by the Office for Product Safety and Standards with criminal enforcement under the Computer Misuse Act and consumer law, and gather any published enforcement notices.
State cyber operations and national security dissertation topics
State-linked hacking mixes crime, national security and international law. Students interested in the laws of armed conflict can add the international humanitarian law topics.
93. Does section 1(2)(e) of the Terrorism Act 2000, which covers action designed seriously to interfere with or disrupt an electronic system, make cyberterrorism a distinct category, and how does it interact with section 3ZA of the Computer Misuse Act 1990?
The definition of terrorism includes serious disruption of electronic systems where the usual purposive elements are met. Compare charging choices and sentencing, and test whether overlapping offences cause confusion. The analysis is doctrinal and works best with a focused set of scenarios.
94. Can a state’s cyber operation below the use-of-force threshold breach the prohibition on intervention, applying Tallinn Manual 2.0 and recent state practice?
The Tallinn Manual is an expert, non-binding study. Examine how states, including the UK, have described sovereignty and intervention in cyberspace, and test hard cases such as election interference and attacks on health services. Keep to published statements and treaties.
95. What standard of proof should the UK Government meet before attributing a cyber operation to a state and imposing cyber sanctions, and could judicial review ever apply?
The Cyber (Sanctions) (EU Exit) Regulations 2020 allow designations tied to cyber activity, and attribution statements are made by the Government and the NCSC. Examine the review provisions in the Sanctions and Anti-Money Laundering Act 2018, and compare attribution practice in other countries.
96. How far do the offences in the National Security Act 2023 on obtaining or disclosing protected information and trade secrets reach state-linked hackers who steal commercial data?
Some offences depend on a foreign power condition, which affects the evidence prosecutors need. Study the statutory definitions and any published charging decisions, then compare the Computer Misuse Act. The topic suits LLM students.
97. Would a power to designate organisations engaged in threatening activity linked to a foreign power, as announced for the Tackling State Threats Bill, cover cybercriminal groups with state ties?
The May 2026 King’s Speech announced the Bill and a designation power. Because the text may not be settled, frame the project around design questions: criteria, evidence, appeal rights and the relationship with proscription. Compare the Terrorism Act 2000 proscription model.
Comparative cybercrime law dissertation topics
Comparative projects work best when each country is chosen for a reason and the legal instrument is named. The context can be adjusted to your own jurisdiction, and a new country on its own is not a new topic.
98. Does the “gates up or down” reading of the Computer Fraud and Abuse Act in Van Buren v United States (2021) offer a better model for “authorisation” than the English approach in section 17 of the Computer Misuse Act 1990?
Van Buren held that a person with authority to access a system does not exceed that authority merely by using it for an improper purpose. Compare the reasoning with Bignell and Allison and with the planned UK reform. Restrict the comparison to the two statutes and the leading cases.
99. How far do EU Member States’ laws implementing Directive 2013/40/EU on attacks against information systems differ on “minor cases” and tools offences, compared with sections 1 and 3A of the Computer Misuse Act 1990?
The Directive requires criminalisation of illegal access, system interference and tools offences, but it leaves Member States some discretion for minor cases. Select three Member States, tabulate their approaches and assess whether differences hinder cooperation. Three countries keep the scope manageable.
100. Is section 26A of Pakistan’s Prevention of Electronic Crimes Act 2016, inserted by the 2025 amendment, a proportionate response to online false information when compared with section 179 of the Online Safety Act 2023?
The Prevention of Electronic Crimes (Amendment) Act 2025, in force from 29 January 2025, inserted section 26A on false or fake information likely to cause fear, panic or unrest, and created a Social Media Protection and Regulatory Authority and a National Cyber Crime Investigation Agency. Compare mental elements, harm thresholds and oversight with the English offence, and apply Article 19 of the International Covenant on Civil and Political Rights as a benchmark.
101. Has the amendment of section 24 of Nigeria’s Cybercrimes Act in 2024 cured the free expression problems identified by the ECOWAS Court of Justice in 2022?
The 2024 Amendment Act, signed on 28 February 2024, rewrote the cyberstalking and false-information provisions after the regional court ordered reform, yet commentators argue vagueness remains and civil society groups have brought further challenges. Compare the text with the 2022 ruling and the African Charter on Human and Peoples’ Rights, using law reports and published litigation as sources.
102. What did Shreya Singhal v Union of India (2015) decide about section 66A of the Information Technology Act 2000, and does it suggest limits for vague “grossly offensive” communications offences, such as those the Online Safety Act 2023 replaced in England?
The Supreme Court of India struck down section 66A for vagueness and chilling effects on speech. Compare the reasoning with the false-message provisions of section 127 of the Communications Act 2003 and the parts of the Malicious Communications Act 1988 that the Online Safety Act repealed. It suits students with access to Indian law reports.
103. How does the African Union Convention on Cyber Security and Personal Data Protection (the Malabo Convention) differ from the Budapest Convention in offences, safeguards and uptake?
Compare the substantive offences, the data protection chapters, the number of ratifications and the institutional follow-up. Use treaty texts and African Union status reports. A regional study suits students from African jurisdictions and works equally well for UK-based comparatists.
Worked examples: from cybercrime law dissertation topics to aims and objectives
Four topics from the list show how a title becomes an aim with testable objectives. The guide to aims, objectives and research questions explains the logic in more detail.
Example from topic 1: a statutory defence for security researchers
Aim: To propose a model statutory defence to section 1 of the Computer Misuse Act 1990 that protects good-faith security research without enabling unauthorised intrusion.
- To analyse the elements of section 1 and the effect of section 17 on authorisation.
- To compare accreditation, authorisation and public interest models using the Government’s 2026 statements and the safe harbours cited in Parliament.
- To draft defence wording and test it against three research scenarios.
Example from topic 25: the associated person test in the failure to prevent fraud offence
Aim: To assess whether the associated person test in section 199 of the Economic Crime and Corporate Transparency Act 2023 captures fraud committed through outsourced providers.
- To set out the statutory definitions and the Home Office guidance of 6 November 2024.
- To apply the test to three outsourcing scenarios.
- To recommend clarifications to guidance for large organisations.
Example from topic 48: how Ofcom judges proportionate measures
Aim: To evaluate how Ofcom applies proportionality when it penalises breaches of illegal content duties under the Online Safety Act 2023.
- To compile Ofcom’s published penalty and confirmation decisions.
- To code the factors Ofcom cites when assessing harm, size and compliance history.
- To compare those factors with the statutory duties and the illegal content codes.
Example from topic 23: reimbursement versus mule prosecutions
Aim: To determine whether mandatory authorised push payment reimbursement reduces scam losses more effectively than criminal enforcement against mule accounts.
- To review the Payment Systems Regulator requirement and its first-year evaluation.
- To analyse published prosecution and conviction data on mule offences under the Proceeds of Crime Act 2002.
- To propose measures that connect reimbursement data with enforcement priorities.
Which method fits a cybercrime law dissertation?
Most cybercrime law projects are doctrinal, but the best ones add one clear second element. The table shows common choices, and the guide to writing a methodology chapter explains how to justify the one you pick.
| Method | Fits best when | Watch out for |
|---|---|---|
| Doctrinal analysis | You are interpreting an Act, a section or a line of cases | Describing the law without arguing a position |
| Law reform analysis | A Bill, consultation or Law Commission paper is live | Treating a proposal as settled law |
| Comparative study | A treaty or another jurisdiction offers a tested model | Choosing more countries than you can read properly |
| Case-law or decision mapping | Reported appeals or regulator decisions are available | Small samples that cannot support a pattern |
| Enforcement or statistical data | Official datasets exist, such as Crime Survey or regulator data | Mixing series that measure different things |
| Interviews with practitioners | The answer depends on how rules work in practice | Ethics approval, access and time |
How to narrow a broad cybercrime idea into a researchable title
Start with the harm, then name the offence or rule, then add the problem, and finally limit the jurisdiction. For example, “ransomware” becomes “paying a ransom”, then “a criminal offence of paying a ransom for public bodies”, then “whether that offence needs a necessity defence in England and Wales”. Each step removes a literature you would otherwise have to review. If you are stuck, the guide to choosing a research topic offers a wider checklist.
Where to find authorities and data for cybercrime law research
- legislation.gov.uk for Acts, regulations and commencement orders.
- Find Case Law and BAILII for judgments.
- Hansard for debates and ministerial statements on reform.
- Crown Prosecution Service legal guidance for charging practice.
- Ofcom and the ICO for enforcement decisions and guidance.
- The Office for National Statistics and the Cyber Security Breaches Survey for prevalence data.
- The Council of Europe cybercrime sites, the UNODC convention site and EUR-Lex for treaty and EU texts.
Common mistakes in cybercrime law dissertations
- Presenting a Bill, consultation or announcement as current law.
- Writing a technical explanation of malware or encryption instead of a legal argument.
- Mixing computer misuse offences with cyber-enabled fraud without saying which one you analyse.
- Relying on press releases or vendor reports where a judgment or statute exists.
- Ignoring jurisdiction, so the argument could apply to England, Scotland or abroad.
- Planning interviews or datasets that cannot be completed within the timetable.
Ethics, safety and university rules
Do not download or handle malware, leaked databases or abuse material for a law dissertation. Rely on statutes, judgments, regulator reports and published data. Interviews with security professionals, police officers or victims normally need ethics approval, and the ethics approval guide explains the usual steps. Many UK law schools expect OSCOLA referencing, but check your own university’s rules, since ethics routes, referencing and marking criteria differ by institution and country.
Cybercrime law dissertation FAQs
Can I write a cybercrime law dissertation about a Bill that has not become law?
Yes, if you label its stage, analyse the text and say what would change. Avoid predicting outcomes, and update your status checks shortly before submission because Bills can be amended or dropped.
Do I need technical skills to write about ransomware or encryption?
Usually not. You need enough understanding to describe the facts accurately, and judgments and regulator reports normally provide that. A short glossary of terms in an appendix can help your reader without turning the project into a computing dissertation.
Is the Computer Misuse Act too old to write about?
No, because its age is the reason reform is under way. However, your project must show a specific gap, such as how a section applies to a modern scenario, rather than repeating that the Act dates from 1990.
Which cybercrime topics need ethics approval?
Projects with human participants, personal data or sensitive content usually need approval, while purely doctrinal projects based on public law usually do not. Confirm the rule with your supervisor, because universities draw the line differently.
Should I choose a doctrinal or a comparative project?
Choose doctrinal if the question is about how one statute or case line works, and comparative if a treaty or another country offers a model you can read in full. Undergraduates often do best with a tightly bounded doctrinal question and one short comparison.
Turn your shortlist of cybercrime law topics into a proposal
Need help narrowing this down? The research question generator can turn a title into a testable question, the aims and objectives generator can draft objectives, and the dissertation topic finder can suggest neighbouring angles. If you would like an adviser to check a shortlist against your marking criteria, law dissertation help is available, and research proposal support can help you shape the proposal itself. Other branches of law are listed in the law dissertation topics by subject.
Use any model or reference material for learning and follow your institution’s academic integrity policy.