Cyber Law Dissertation Topics: 108 Free, Narrow Ideas on Data, AI, Platforms and Digital Assets
Cyber law dissertation topics work best when the title already names an Act, a case or a date, because a narrow title tells your supervisor you have read the source and not just the headline. Every idea below does that. Each one is free to use, and each comes with a short note on method, comparison or caution so you can see what the project would actually involve.
You have probably chosen your degree and now face the harder part: finding a cyber law topic that is current, narrow and doable in one dissertation. If that sounds familiar, these are the questions this guide answers:
- Which cyber law topic is narrow enough to finish in a single dissertation, and not so narrow that there is nothing to argue?
- Which statutes, cases and regulator decisions are current this term, so my literature review is not already out of date?
- Can I compare the UK with the EU, the US or my own country without doubling my workload?
- Should my method be doctrinal, comparative or empirical, and what evidence can I realistically reach?
- What do I do if the law changes between my proposal and my submission?
Scope: this list covers data protection, online platforms, AI and copyright, cybersecurity regulation, digital assets, digital consumer and competition law, and cross-border questions. Hacking, fraud and other offences sit in the separate guide to cybercrime law topics (linked in the cybersecurity section below), so the two lists do not overlap.
Position correct as of October 2026. Several items below depend on appeals, Bills or EU negotiations that were still open at that date. Where that is the case, the note says so, and the headline is worded around the lasting legal question so it will not go stale.
Data protection and privacy: cyber law dissertation topics after the 2025 Act
Data protection is the busiest corner of cyber law dissertation topics right now, because the UK rewrote parts of UK GDPR in 2025 while the EU kept its own rulebook and its own court. The Data (Use and Access) Act 2025 is the main source here, and its commencement is staged, so state in your methodology which provisions were in force on your cut-off date.
- Does the recognised legitimate interests list in Article 6(1)(ea) UK GDPR, added by the Data (Use and Access) Act 2025, weaken the balancing test that Article 6(1)(f) normally requires? A doctrinal question with an easy comparison point: the EU has no equivalent list. Your argument could turn on whether pre-approved purposes such as crime prevention or safeguarding make controllers lazy about proportionality.
- How far do the new Articles 22A to 22D on automated decision-making protect individuals compared with the old Article 22 prohibition? The 2025 Act replaces a general bar with safeguards for significant decisions, and keeps tighter rules where special category data is used. Compare it with how the CJEU read Article 22 in SCHUFA (C-634/21).
- What does the complaints-handling duty placed on controllers by the 2025 Act change for data subjects, and does it risk adding a hurdle before the regulator will act? Good for a policy analysis. You can test it against the ICO’s own published complaint statistics, which makes the project empirical without needing ethics approval for interviews.
- Does turning the Information Commissioner into a board-led Information Commission strengthen or dilute regulatory independence, measured against the independence tests in Article 52 of the EU GDPR? The EU test matters because the UK’s adequacy status depends on it. A short comparative chapter on how other regulators are governed would give the argument weight.
- Will aligning PECR fines with UK GDPR levels change how cookie and direct marketing breaches are enforced in practice? Look at past ICO penalties under the Privacy and Electronic Communications Regulations and ask whether the old £500,000 ceiling really limited enforcement or whether resources were the real constraint.
- Do the new cookie consent exemptions for analytics and similar low-risk purposes fit the logic of the ePrivacy Directive 2002/58, or do they move the UK further from the EU model? Method: comparative statutory reading, with one worked scenario such as a news site using audience measurement.
- What does the General Court’s dismissal of Latombe v Commission (T-553/23) reveal about how closely EU courts will scrutinise adequacy decisions, and what would an equivalent challenge to the UK decision look like? An appeal (C-703/25 P) was lodged, so check its stage before you write the final chapter and frame your conclusion around the legal test rather than the outcome.
- Are supplementary measures and transfer risk assessments, as developed after Schrems II (C-311/18), realistic for small UK exporters using the International Data Transfer Agreement? Because the question is about practice, a short survey of compliance officers or a review of published ICO guidance would give you primary material.
- After Lloyd v Google [2021] UKSC 50, is any route left for opt-out representative actions over loss of control of personal data in England and Wales? Read it alongside the Court of Appeal and High Court decisions that followed, and ask whether the group litigation order or the Part 19 route does the same job.
- Where does the line fall on compensation for non-material damage under Article 82 GDPR after Österreichische Post (C-300/21), and has English case law tracked it? A tidy comparison between the CJEU’s no-threshold approach and English courts’ reluctance to compensate trivial distress.
- What risk of disclosure is enough to found a data protection compensation claim in Farley v Paymaster (trading as Equiniti)? Equiniti’s mis-sent benefit statements raised the threshold question for fear of misuse. The case was heading to the Supreme Court, so check the judgment status and treat the pending outcome as a live gap.
- Can the ICO’s jurisdiction over a foreign web scraper, tested in the Clearview AI litigation, be reconciled with the territorial scope in Article 3 UK GDPR? Verify the current appeal position first. The enduring issue is whether monitoring behaviour of people in the UK can ever be separated from the scraper’s place of business.
- Can legitimate interests under Article 6(1)(f) justify scraping personal data to train generative AI models, taking EDPB Opinion 28/2024 and the ICO’s guidance as the yardstick? A comparison chapter works well here. Contrast the ICO’s more permissive tone with the EDPB’s stricter reading of necessity and reasonable expectations.
- How do the ICO’s Children’s Code and the Online Safety Act’s age assurance duties overlap, and where do they pull in opposite directions on data minimisation? Age checks need data; the Code asks for less of it. This tension is the heart of the project, so build your research question around one specific service type such as a video platform.
- Does the 2025 Act’s ‘reasonable and proportionate search’ standard for subject access requests settle the Dawson-Damer line of cases or just restate it? Needs close reading of the pre-2025 case law. Consider interviewing a DPO or two if your university’s ethics process allows it.
- Does the right to an explanation of automated decision logic recognised in Dun & Bradstreet Austria (C-203/22) clash with trade secret protection under Directive 2016/943? The CJEU said the controller must explain the procedure and principles applied, not hand over the algorithm. Test where that leaves credit scoring firms.
- Is pseudonymised data personal data in the recipient’s hands, following the CJEU’s relative approach in EDPS v SRB (C-413/23 P)? A narrow, manageable project. Apply the test to a concrete data-sharing arrangement such as research data held by a university.
- Is Meta Platforms v Bundeskartellamt (C-252/21) a sound basis for letting competition authorities assess GDPR compliance? Links data protection to competition law, which suits students whose degree covers both. Compare with the DMA’s own Article 5(2) data combination rule.
- Can ‘consent or pay’ advertising models meet the freedom-of-consent standard in EDPB Opinion 08/2024 on large online platforms? A clean legal-analysis topic with a growing number of regulator decisions to evaluate.
Online safety and platform liability: cyber law dissertation topics for LLM and law students
Platform regulation produces some of the most current cyber law research topics, mainly because regulators now publish decisions and codes rather than just guidance. Anchor each project in one instrument, such as the Online Safety Act 2023 or the EU Digital Services Act, and say which enforcement documents you are treating as primary sources.
- Is Ofcom’s proportionate approach to small but high-risk services in the illegal content codes of practice workable under the Online Safety Act 2023? You can test it by taking three real small services and mapping their features to the code’s measures. It sidesteps legal speculation by relying on published documents.
- Was it right to treat the Wikimedia Foundation as a possible Category 1 service in R (Wikimedia Foundation) v Secretary of State [2025] EWHC 2086 (Admin), and what does the case show about how thresholds should be drafted? Read the High Court judgment first, then ask what design alternatives the regulations could have used for non-profit, community-moderated services.
- To what extent does mandatory age assurance for pornography and harmful content, in force since July 2025, breach Article 8 ECHR privacy rights? A proportionality analysis. Include the technical options such as facial age estimation and open banking checks, because the legal question changes with the method.
- What does Ofcom’s published enforcement activity involving X’s Grok tool show about how the Online Safety Act applies to generative AI features inside a social platform? Treat the investigation documents as your data set and check the current status before writing up, because decisions in this area move quickly.
- Can technical capability notices under the Investigatory Powers Act 2016 lawfully force a provider to weaken end-to-end encryption, as the Apple and Home Office dispute before the Investigatory Powers Tribunal suggests? Fine-grained question about statutory purpose and necessity. Compare it with section 121 of the Online Safety Act on notices to identify child sexual abuse material.
- Does the proposed EU regulation on preventing child sexual abuse online, often called Chat Control, meet the proportionality test the CJEU applied in Digital Rights Ireland (C-293/12)? The legislative text has changed repeatedly, so anchor your analysis in the proportionality test and cite the version you analysed.
- How do the 48-hour removal duty and the FTC enforcement of the Take It Down Act fit with the First Amendment and the immunity in section 230 of the Communications Decency Act? The FTC announced enforcement in 2026, which gives you a fresh regulator to study. Compare with the UK’s treatment of intimate image abuse in the Online Safety Act.
- Does Article 6 of the Digital Services Act preserve the hosting safe harbour in a way that differs materially from section 230? A classic comparative project. Add the ‘Good Samaritan’ protection in Article 7 DSA as a distinguishing point.
- How effective are the Commission’s formal proceedings against X under the Digital Services Act in enforcing Article 34 systemic risk assessment duties? Method: case study of the preliminary findings and the company’s replies. Keep the focus on legal reasoning rather than politics.
- Do out-of-court dispute settlement bodies under Article 21 of the Digital Services Act give users a real remedy against content moderation decisions? Lends itself to a small empirical angle, such as reading published transparency reports from certified bodies.
- Can the fraudulent advertising duty on the largest services under the Online Safety Act cut online scams, and what does it need to work? Assess it against the Payment Systems Regulator’s reimbursement scheme to see whether the burden is being shared sensibly.
- Is the false communications offence in section 179 of the Online Safety Act compatible with Article 10 ECHR? A speech question for students who prefer constitutional law. Compare with the repealed section 127 of the Communications Act 2003.
- What can the UK learn from Australia’s social media minimum age law, in force from December 2025, when deciding whether to restrict under-16 access to platforms? UK proposals on under-16 rules were still developing, so use Australia as the tested example and treat the UK as the proposed one.
- Does the website operators’ defence in section 5 of the Defamation Act 2013 still protect platforms now that the Online Safety Act has added proactive duties? Reading the 2013 Regulations alongside the Ofcom codes shows where notice-and-takedown logic and risk-based logic collide.
- How far did NT1 and NT2 v Google [2018] EWHC 799 (QB) extend the Google Spain (C-131/12) right to delisting, and has it survived in UK law after Brexit? A history-and-law project. Retained EU law reforms make the post-Brexit status a real question.
- How should Article 27 and Article 38 of the Digital Services Act regulate recommender systems, and does a non-profiling option change what users see? You can pair legal analysis with an audit of what one platform offers as its non-profiling feed.
AI, copyright and liability: cyber law research topics that need new answers
Artificial intelligence has produced the fastest-moving set of cyber law research topics, and it overlaps with intellectual property law dissertation topics and the wider artificial intelligence dissertation topics list. Judgments here are being appealed or replaced quickly, so frame each project around the legal question that will outlast any single ruling.
- Is a trained model’s weights an ‘infringing copy’ for the purposes of secondary infringement in sections 22 and 23 of the Copyright, Designs and Patents Act 1988, as argued in Getty Images v Stability AI? The High Court gave its decision in November 2025 and an appeal was expected, so check where it stands. The enduring puzzle is whether an article can be an infringing copy if it never stores the work.
- Can the text and data mining exception in section 29A CDPA 1988 survive in its non-commercial form, given the government’s copyright and AI consultation and the consultation and impact assessment? Pair it with the reporting duties on copyright and AI in the 2025 Act. You could compare the options the government weighed using its own cost and benefit tables.
- Does section 9(3) CDPA 1988, giving 50 years of protection to computer-generated works, still serve any purpose now that generative AI exists? A short, sharp doctrinal topic. Tie it to the originality tests in Infopaq (C-5/08) and the ‘author’s own intellectual creation’ standard.
- Should AI systems be named as inventors? Re-examining Thaler v Comptroller-General [2023] UKSC 49 against recent policy proposals on AI-assisted inventions. Only a human can be an inventor under the Patents Act 1977, but policy bodies have asked whether the law should change. Compare the Thaler line in the US and the EPO.
- What does Thaler v Perlmutter (D.C. Cir. 2025) establish about human authorship, and how does it compare with the UK’s computer-generated works rule? Good for a comparative chapter. Add the US Copyright Office’s guidance on AI-assisted works as your secondary source.
- How should GPAI providers meet the copyright policy and training data summary duties in Article 53 of the EU AI Act? The Code of Practice for general-purpose AI is the practical benchmark. Method: compare published training summaries from two providers.
- Is delaying the high-risk obligations of the EU AI Act through the Digital Omnibus on AI consistent with legal certainty and the principle of proportionality? The omnibus was still moving through trilogue, so state your cut-off date. The enduring question concerns how law can be postponed once businesses have prepared.
- Does the Munich Regional Court’s 2025 decision in GEMA v OpenAI on lyrics memorisation provide a workable test for when a model ‘contains’ a protected work? Read the judgment in German if you can, or an official summary if not. Contrast with the English Getty analysis.
- Can press publishers rely on the neighbouring right in Article 15 of the DSM Directive against a chatbot, as the Hungarian reference in Like Company v Google (C-250/25) asks? A pending reference, so build your argument around the questions referred rather than a prediction.
- Do the fair use rulings in Bartz v Anthropic and Kadrey v Meta (N.D. Cal., 2025) give training a safe harbour, and would the same facts succeed under UK fair dealing? A neat transatlantic comparison. Analyse the purpose and effect factors in the US cases against the narrower fair dealing purposes in sections 29 to 30A CDPA.
- Did Thomson Reuters v Ross Intelligence (D. Del. 2025) draw a workable line between generative and non-generative AI training? The court distinguished a non-generative legal search tool, so this is a tight case study of how far that reasoning stretches.
- Is there a case for a statutory personality or likeness right in England and Wales, drawing on Denmark’s proposal to treat a person’s likeness as copyright-protected? UK law has no image right, and passing off is awkward for private individuals. Check the stage of the Danish bill before citing it.
- Where does liability fall when a chatbot gives wrong advice, as in Moffatt v Air Canada (2024 BCCRT 149)? The tribunal rejected the airline’s argument that the chatbot was a separate entity. Explore how a UK court might handle the same facts under the Consumer Rights Act 2015 and negligent misstatement.
- What professional duties follow from fabricated AI citations in court, as set out in Ayinde v London Borough of Haringey [2025] EWHC 1383 (Admin)? Read the Divisional Court judgment and ask whether the response should rest on regulators’ guidance or statutory duties. Good for students on a legal practice route.
- Can an AI developer be liable in defamation for hallucinated statements, taking Walters v OpenAI (Ga. Super. Ct. 2025) as the starting point? The court granted summary judgment to OpenAI, so your project could test whether the English serious harm threshold in section 1 of the Defamation Act 2013 would lead to a different answer.
- Does the new Product Liability Directive (EU) 2024/2853, which treats software as a product, adequately cover harm caused by AI systems after the withdrawal of the AI Liability Directive? Member states had until December 2026 to transpose the Directive. Method: analysis of the disclosure and presumption mechanisms in Articles 9 and 10.
- Is the Court of Appeal’s reasoning on live facial recognition in R (Bridges) v Chief Constable of South Wales [2020] EWCA Civ 1058 still adequate now that the government is consulting on a statutory framework? The Home Office consultation opened a policy window. Treat any Police Reform Bill provisions as pending until you have verified the current text.
Cybersecurity regulation: cyber law topics on duties, liability and resilience
Cybersecurity law gives students a different texture, with statutes that impose duties on organisations rather than on attackers. This section sits next to cybersecurity dissertation topics for technical readers, and keeps the focus on legal duties, regulators and liability. For offences and prosecution, use the separate cybercrime law dissertation topics list instead.
- How should the Cyber Security and Resilience Bill widen the Network and Information Systems Regulations 2018 to cover managed service providers and data centres? The Bill was still before Parliament, so state its stage on your cut-off date. The enduring question is whether supply chain risk can be regulated through designation rather than contract.
- Does the incident reporting timetable in the Cyber Security and Resilience Bill match the practical limits of a victim organisation’s first 24 hours? Combine a reading of the Bill with interviews or published incident reports from the 2025 retail and automotive attacks.
- How far does personal liability of management bodies under Article 20 of NIS2 change boardroom behaviour compared with the UK’s NIS Regulations? Use Article 21’s risk management list as the yardstick, and consider a comparative view of two member states’ transposition laws.
- When must manufacturers report actively exploited vulnerabilities under the Cyber Resilience Act, and does the September 2026 start date leave businesses enough time? The national guidance on the Act is a helpful anchor. Frame the question around Article 14 and the single reporting platform.
- Is the ‘open-source steward’ category in Article 24 of the Cyber Resilience Act a workable compromise for volunteer-run projects? A niche but publishable topic that sits between law and software engineering. Interview maintainers if you can, or use published foundation responses.
- Does the Digital Operational Resilience Act‘s oversight of critical ICT third-party providers deliver more than the UK’s critical third parties regime under FSMA 2023? A good financial-regulation crossover. Compare the designation criteria, the information powers and the sanction mechanisms.
- Can the Telecommunications (Security) Act 2021 and its code of practice deliver supply chain security without the compensation questions raised by removing high-risk vendors? A mix of statute and public law. Look at the human rights angle around property under Article 1 of Protocol 1.
- Has banning default passwords through the Product Security and Telecommunications Infrastructure Act 2022 and its 2023 regulations been enforced in any meaningful way? A neat empirical topic. Search the Office for Product Safety and Standards for published enforcement and compliance data.
- Does the proposed UK ban on ransomware payments by public bodies and critical infrastructure operators fit with sanctions rules that apply strict liability under OFSI? Pair the policy proposals with OFSI’s penalty guidance to see how a victim could face conflicting duties.
- Can the SEC’s cybersecurity disclosure rules (Form 8-K Item 1.05) and the SolarWinds litigation over CISO liability be reconciled with a workable standard of ‘material’ incidents? Check how the SEC case ended before you cite it. The enduring question is how securities law copes with cyber risk.
- Did the ICO’s monetary penalty on Capita after the 2023 breach clarify what ‘appropriate technical and organisational measures’ means under Article 32 UK GDPR? Build a table of the ICO’s fines for security failures and look for patterns. Verify the final penalty amount from the ICO notice.
- Does the war exclusion in cyber insurance survive Merck v ACE (N.J. App. Div. 2023), and how should the UK market’s Lloyd’s state-backed attack clauses be read? A contract-law project with commercial reach. Compare the Merck wording with Lloyd’s Market Bulletin Y5381.
- When can a state be said to breach the rule of sovereignty through a cyber operation, and why does the UK reject sovereignty as a standalone rule of international law? Read the UK Attorney General’s 2018 speech against the Tallinn Manual 2.0 commentary. A strong choice for public international law students.
- How does the Second Additional Protocol to the Budapest Convention, with its direct disclosure provisions in Article 7, reshape cross-border access to subscriber data? Compare it with the CLOUD Act framework. Use the Council of Europe’s explanatory report as your core text.
- Does the UK-US Data Access Agreement under the CLOUD Act give UK investigators faster results than mutual legal assistance, and does it respect UK data protection standards? A black-letter piece that benefits from official reports on use of the agreement.
- What does the EU e-Evidence Regulation 2023/1543, applicable from August 2026, change for service providers who receive production orders from another member state? Cover the 10-day and 8-hour deadlines and the role of the notification procedure. Compare with the UK’s Crime (Overseas Production Orders) Act 2019.
Digital assets and smart contracts: cyber law dissertation topics on property and code
Digital asset law is a good fit for students who want doctrinal depth, because English law recently gave the subject a statutory footing. Related reading sits in blockchain dissertation topics and cryptocurrency dissertation topics, which lean towards technology and markets rather than the law.
- What does the third category of personal property created by the Property (Digital Assets etc) Act 2025 change for insolvency and succession, compared with the old common law choses framework? A short statute with plenty of unanswered questions. Method: read the Law Commission’s reports that led to it and test the Act against two hypothetical estates.
- Which law governs a dispute over a cryptoasset held on a decentralised ledger, and what do the Law Commission’s private international law proposals add? The Law Commission’s project is still the best starting point. Check whether a final report has appeared before you finalise your chapter plan.
- Do open-source developers owe fiduciary duties to cryptoasset owners, as Tulip Trading v van der Merwe [2023] EWCA Civ 83 allowed to be argued? The case was a jurisdiction and strike-out decision, so read carefully what was decided and what was left open.
- Is service of proceedings by NFT airdrop, allowed in D’Aloia v Persons Unknown [2022] EWHC 1723 (Ch), a sound extension of alternative service under CPR 6.15? Practical civil procedure with a technology twist. Compare other English orders that allowed email or social media service.
- Are proprietary injunctions against persons unknown in crypto fraud cases, beginning with Ion Science v Persons Unknown (2020), consistent with the requirement of a real prospect of recovery? Check the later case law on Bankers Trust orders against exchanges and map the range of relief.
- Should smart legal contracts need their own statute, or does the Law Commission’s 2021 conclusion that existing contract law copes still stand? Select one example, such as a parametric insurance contract, and test it against offer, acceptance and mistake.
- Does MiCA‘s white paper liability in Article 15 give investors a better remedy than the English misrepresentation regime? Consider the transitional deadline of July 2026 for existing providers, and compare it with the FCA’s cryptoasset regime as it develops.
- How should the UK’s planned cryptoasset regime under the Financial Services and Markets Act 2000 treat staking and decentralised finance, which have no obvious intermediary? Policy-heavy. Check the HM Treasury and FCA documents for the current position before you start.
- Was the Fifth Circuit right in Van Loon v Department of the Treasury (2024) to say that immutable smart contracts are not ‘property’ that can be sanctioned? A stimulating case for students who like arguing about what ‘property’ means. Compare with the English Act’s focus on ‘things’.
- Can a decentralised autonomous organisation be a general partnership, as Sarcuni v bZx (S.D. Cal. 2023) allowed, and what would English partnership law say? Apply the Partnership Act 1890 to a DAO’s governance token holders and see whether limited liability could be achieved through a Wyoming-style structure.
- Did the MetaBirkins decision in Hermès v Rothschild (S.D.N.Y. 2023) treat NFTs as expressive works or as source indicators? Combine the Rogers test with the UK’s likelihood-of-confusion analysis under section 10(2) of the Trade Marks Act 1994.
- Does the Electronic Trade Documents Act 2023 give electronic bills of lading the same legal effect as paper ones, and who carries the risk of a platform failure? Great for students with a maritime or trade finance angle. See also maritime law dissertation topics for adjacent ideas.
- Will the EU Digital Identity Wallet, due from member states by the end of 2026, sit comfortably alongside the UK’s digital verification services framework in the Data (Use and Access) Act 2025? A comparative identity law project. Note that mutual recognition will depend on trust frameworks as well as on technology.
- Is the ‘compliance by design’ approach to e-signatures in the Electronic Communications Act 2000 and the Law Commission’s 2019 report still adequate for remote execution of deeds? A practical conveyancing question. Include a short analysis of witnessed e-signature guidance.
Consumer, competition and platform contracts: cyber law topics for commercial law students
Commercial lawyers will find plenty of cyber law topics where digital markets meet consumer protection. If your degree leans towards markets, pair this section with competition law dissertation topics for the competition side of each question. The Digital Markets, Competition and Consumers Act 2024 is a central source, and some of its commencement dates came later than Royal Assent.
- Does the ban on fake reviews in the Digital Markets, Competition and Consumers Act 2024 give the CMA effective tools against review farms? The ban took effect in April 2025. A neat empirical angle is to track CMA enforcement announcements since then.
- Will the subscription contracts regime in the 2024 Act end subscription traps, or will traders simply redesign the cancellation journey? Pair a reading of the secondary legislation with screenshots of live cancellation flows at three companies. Check the commencement date before you begin.
- Is the CMA’s strategic market status designation process under Part 1 of the 2024 Act consistent with the fairness and appeal standards in judicial review? The CMA made its first designations in 2025. Focus on the appeal standard rather than the economics.
- Does the Digital Markets Act‘s ban on combining personal data in Article 5(2) overlap with, or exceed, GDPR consent rules? The Commission’s 2025 decision against Meta’s pay or consent model gives you a concrete example.
- What does the Commission’s 2025 non-compliance decision against Apple tell us about the anti-steering rule in Article 5(4) of the Digital Markets Act? The decision includes a fine and orders about app store communications. Treat appeals as pending.
- How far does Article 32 of the Data Act protect non-EU cloud customers from foreign government access requests? Compare it with Article 48 GDPR and the CLOUD Act. A lively but narrow subject.
- When do cloud switching charges end under Chapter VI of the Data Act, and do the transition periods favour incumbent providers? The Data Act has applied since September 2025 and charges phase out by January 2027. The sector interviews published by the Commission offer useful evidence.
- Do the digital content provisions in sections 33 to 47 of the Consumer Rights Act 2015 give a consumer a meaningful remedy for a defective app or game? Reading the remedy hierarchy against real app store terms helps you assess how many consumers can actually use it.
- Are browsewrap terms binding after Nguyen v Barnes & Noble (9th Cir. 2014), and how would an English court approach the same facts? Use the incorporation rules in Parker v South Eastern Railway and the Consumer Rights Act’s fairness test.
- Do the dark patterns prohibited in Article 25 of the Digital Services Act and the drip pricing rules in the 2024 Act cover the same ground? The FTC’s 2025 settlement with Amazon over Prime enrolment illustrates the US enforcement route.
- Does L’Oréal v eBay (C-324/09) still describe when an online marketplace becomes liable for sellers’ trade mark infringements after the Digital Services Act? Compare it with Coty v Amazon (C-567/18) on storage and the DSA’s article 6 hosting protection.
- Which court has jurisdiction over online personality rights, comparing eDate Advertising (C-509/09) with Lachaux v Independent Print [2019] UKSC 27 on serious harm? Tests how English and EU courts treat the same internet publication differently.
- Does the Hague Judgments Convention 2019, in force for the UK since July 2025, change the enforceability of English judgments against online defendants? Comparative private international law. Check the exceptions list and whether the other state is a party.
- Can net neutrality survive zero rating after Telenor Magyarország (C-807/18) and the BEREC guidelines? A short competition-meets-telecoms analysis with real-world tariff examples.
Jurisdiction, surveillance and international comparison: cyber law dissertation topics beyond the UK
Students based outside the UK, or comparing two systems, can use this group of cyber law dissertation topics. Instruments come from different countries, but each topic is a different legal question, not a country swap. Many intersect with human rights law dissertation topics and EU law dissertation topics.
- Does the bulk interception regime of the Investigatory Powers Act 2016 meet the end-to-end safeguards set by Big Brother Watch v UK (Grand Chamber, 2021)? A strong human rights project. The UK’s Act has been amended since, so compare the original and updated provisions.
- Should courts order worldwide delisting or takedown, comparing Google v CNIL (C-507/17), Glawischnig-Piesczek (C-18/18) and Google v Equustek [2017] SCC 34? Three leading decisions that disagree. Frame the project around territorial limits and comity.
- Can civil liability for spyware vendors, as in WhatsApp v NSO Group (N.D. Cal. 2024 to 2025), be mirrored under English law or EU law? Needs careful research into which causes of action apply outside the US Computer Fraud and Abuse Act.
- How do the cross-border transfer mechanisms in Article 38 of China’s Personal Information Protection Law and the equivalent regime in India’s Digital Personal Data Protection Act 2023 compare with the GDPR’s adequacy model? A comparative piece with Asia-focused sources. Check the status of the implementing rules in each country.
- Does the Nigeria Data Protection Act 2023 adopt the GDPR’s model closely enough to count as an adequacy candidate? Look at the Act’s provisions on cross-border transfers and the Commission’s enforcement record to date.
- Has the 2025 amendment to Pakistan’s Prevention of Electronic Crimes Act 2016, which created a social media regulatory authority, balanced speech and platform accountability? A pointed topic for students in or from Pakistan. Use the Act’s text and judgments of the High Courts rather than commentary alone.
- How does the UAE’s Federal Decree-Law No. 45 of 2021 on personal data protection compare with the GDPR on consent and cross-border transfers? Verify translations carefully and rely on official Arabic text or accredited English versions.
- What limits does Brazil’s LGPD place on public sector data sharing compared with the UK’s Digital Economy Act-based data sharing powers and the new 2025 Act gateways? Brings together administrative law and data protection. Pick a single policy area such as health or tax data.
- Do the American state privacy laws, led by the California Consumer Privacy Act as amended by the CPRA, achieve the same protections as GDPR without a federal law? Choose two or three states and compare enforcement approaches rather than every state.
- Are internet shutdowns compatible with Article 19 ICCPR, as the ECOWAS Court found in Amnesty International Togo v Togo (2020)? A rights-based project that rests on a short, readable judgment. Add Access Now’s shutdown data as an evidence set.
- Does the Council of Europe’s Framework Convention on Artificial Intelligence add anything to the EU AI Act for rights protection? A treaty-interpretation project. Note the exemptions for national security.
- Is the UN Convention against Cybercrime, signed in Hanoi in 2025, compatible with the human rights safeguards in Article 15 of the Budapest Convention? Concentrate on the safeguards and data sharing provisions, not on criminal offences.
How to choose between these cyber law dissertation topics
The right cyber law dissertation topic is the one where you can reach the evidence in the time you have. Use this table to match the method to the sources before you commit.
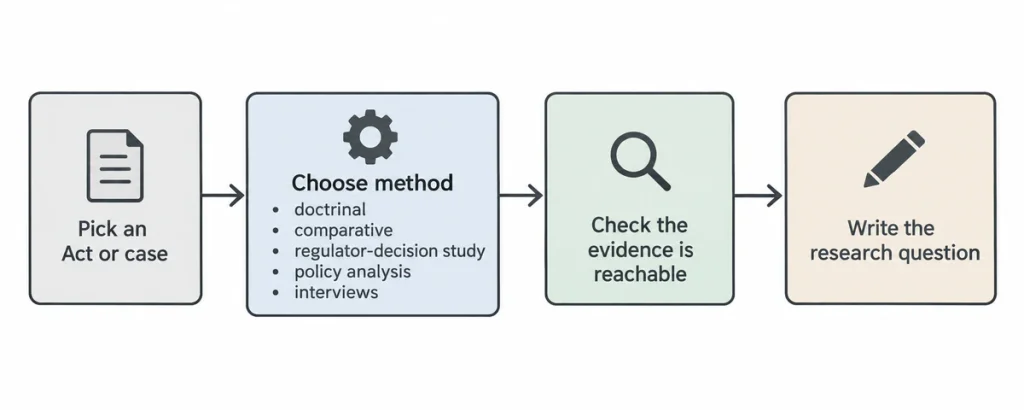
| Method | Suits | Where the evidence is |
|---|---|---|
| Doctrinal analysis | A statute, a section or a line of cases, such as the 2025 Act or Getty v Stability | UK legislation and judgments through Find Case Law and legislation.gov.uk; EU texts on EUR-Lex |
| Comparative law | Two systems answering one question, such as UK against EU or UK against US | Official gazettes, court websites and the regulators’ own decisions |
| Regulator-decision study | Enforcement trends, for example Ofcom, the ICO or the Commission | Ofcom’s online safety publications and ICO enforcement notices |
| Policy analysis | A Bill, consultation or impact assessment still moving | Hansard, committee reports and government consultation responses |
| Interviews or surveys | Practice questions such as compliance duties or incident reporting | Needs ethics approval; plan the sample early and keep it small |
Whatever you pick, check your own university’s rules on ethics approval, referencing style and word limits, because they differ between institutions and countries. The ethics approval guide explains the usual steps.
Turning cyber law dissertation topics into a research question
A good cyber law dissertation topic still needs a question that can be answered with evidence. Three quick patterns work well for the ideas above:
- Test a rule against a standard. Take the recognised legitimate interests list and ask whether it meets the proportionality logic of Article 6(1)(f). The answer needs the statute, two or three authorities and a clear criterion.
- Compare two answers to one problem. Set the Getty Images v Stability AI reasoning on infringing copies beside the US fair use rulings, and say which one handles model weights better and why.
- Follow an enforcement trail. Read ten published Ofcom or ICO decisions, code them against the duties in the Act, and report what the regulator actually prioritises.
The guide on how to write a research question breaks these steps down, and the research question generator gives you a quick first draft to refine.
Cyber law dissertation topics: common questions
What counts as a cyber law dissertation topic?
Any legal question about digital technology, data, online platforms, AI or electronic transactions. Cyber law dissertation topics usually centre on a statute, a regulator or a leading case, and they can be doctrinal, comparative or empirical.
Are these cyber law topics free to use?
Yes. Every topic here is free for anyone to use, adapt or combine, and you do not need to register or pay.
Which topics suit an LLM dissertation?
Comparative ones tend to work best, such as the EU AI Act against UK copyright reform, or the Digital Services Act against the Online Safety Act. They give you two systems, a clear method and enough primary material for a Master’s level project.
Do I need ethics approval for a cyber law dissertation?
Not for purely doctrinal work based on public legislation and judgments. You usually will if you interview practitioners or survey students, so ask your supervisor early.
How do I handle law that changes while I write?
State a cut-off date in your introduction, note anything pending in a short limitations paragraph, and re-check your key authorities a week before you submit.
Can I compare the UK with my own country?
Yes, provided you pick one legal question and two instruments that answer it. Avoid trying to cover every difference between the two systems.
Next step: shape one topic into a proposal
Pick two topics that you could imagine arguing about for a year, then check that the main sources are reachable. A proposal that names its Act, case and method is easier to approve, and the guide to the dissertation proposal shows how to lay it out.
If you want a topic fitted to your own degree, the dissertation topic finder narrows the options, and our custom dissertation topics service tailors them to your course. Other law students may also want the main law dissertation topics list. For hands-on support with the methodology chapter or the full project, Help With Dissertation offers law dissertation help and dissertation methodology help.