Information Systems Management Dissertation Topics: Narrow Titles with Real Data Routes
Which information systems management topic fits what you can research?
Strong information systems management dissertation topics name a system, a setting, an outcome and a source of evidence. Before you commit to a title, settle these questions for yourself:
- Which system or process am I studying: an ERP platform, a legacy estate, a cloud contract, an AI tool or a security programme?
- Which organisation or sector will give me access, and who has to approve it?
- Am I explaining adoption, governance, delivery or risk, and which theory or framework fits that choice, such as TAM, COBIT or the NIST Cybersecurity Framework?
- Can I measure the outcome with data I can reach, such as tickets, survey answers, annual reports or ONS tables?
- Does my topic depend on a rule that is still changing, such as a Bill before Parliament or an EU deadline?
- Is my idea about managing systems or about building them, and would a computing project suit it better?
- What will I cut if interviews are refused or data arrives late?
These topics concentrate on how organisations choose, run, govern and secure information systems: enterprise platforms, legacy IT, governance, data rules, cloud sourcing, AI use and user behaviour. If your project centres on writing code or designing networks, the information technology dissertation topics resource is the closer fit. Analytics-heavy ideas sit better with the data science dissertation topics list. For wider organisational questions, see the management dissertation topics overview. Check your own university’s rules on ethics, referencing and marking, because they differ between countries and schools.
Position correct as of October 2026. Several topics below rely on rules and programmes that are still moving, including the Cyber Security and Resilience (Network and Information Systems) Bill, EU AI Act timelines, UK e-invoicing and digital identity plans. Check the named official source before you state any status in your own work.
Information systems management dissertation topics by research area
Numbering runs continuously from the first topic to the last. Each title names a system, rule, dataset or setting, so you can test it quickly against your access, level and timeline. As a rough guide, undergraduate projects usually take one organisation or one set of documents. Master’s projects can compare cases or test a model. PhD projects need a clear theoretical contribution.
Delivery, project governance and failure analysis
Projects that focus on project methods more than on the system itself may also suit the project management dissertation topics list.
1. Reading the Post Office Horizon IT Inquiry as an IT governance case: what published evidence shows about challenge and escalation inside a contracted system programme. Volume 1 of the final report, published on 8 July 2025, covers human impact and redress, and a later volume is expected to address causes and accountability. Check on the inquiry’s publications list which parts are out before you fix your scope. Document analysis of witness statements and board papers, coded against a governance framework such as COBIT, suits a Master’s project. Treat the subject with care, because it involves wrongful prosecutions and serious harm to postmasters and their families.
2. Escalation of commitment in publicly reported IS programme resets: coding committee reports for sunk-cost and “one more phase” language. Keil and colleagues built much of the research on why troubled software projects keep receiving money, so you can use their ideas as a coding scheme. Pick four to six programmes with public committee reports. Code only documents dated before each reset decision, because hindsight bias is the main threat to this design.
3. Benefits realisation after go-live: tracing the original business case through later committee papers for one council system replacement. Council committee papers are public, so you can usually follow the approved budget, the promised benefits and later variation reports without interviews. An undergraduate version can track three promised benefits for one replacement, such as a housing, revenues or case management system. Add a short interview with a project manager if access allows.
4. Do delivery metrics predict stability? Applying the DevOps Research and Assessment measures (deployment frequency, lead time, change failure rate and time to restore) to one team’s release history. These DevOps measures share an acronym with the EU Digital Operational Resilience Act but have nothing to do with it. Use ticket and deployment logs with written permission. Limit the study to one team over twelve to eighteen months and report descriptive trends before any test, since a single team gives a small sample.
5. Change advisory boards and release frequency in a regulated organisation: whether approval steps reduce incidents or only delay releases. Combine incident records with interviews about how approval decisions are really made. Gatekeeper approval and anonymisation matter here. If access is narrow, cut the scope to one service line.
6. Data migration reconciliation in a system replacement: how control totals, sampling and exception reports find errors before cut-over. Design science suits a Master’s project. Build a reconciliation checklist, test it on a synthetic or anonymised extract and evaluate it with practitioners. An undergraduate version could compare three published migration approaches against one checklist.
7. Knowledge retention after outsourced implementation: what an internal team can still explain twelve months after the supplier leaves. Interview five to eight staff and audit the handover documentation, then analyse both with thematic analysis. The risk is that the people who remember most have already left, so ask early who has moved on.
8. User acceptance testing led by business staff: whether test effort before go-live relates to defects raised in the first 90 days. You need access to the defect log and test records. Compare modules while allowing for module complexity, and keep claims modest because the number of modules is usually small.
9. Low-code applications built by non-IT staff in universities: who approves them, who supports them and what happens when the builder leaves. Survey IT directors and administrators, then use Weill and Ross’s decision-rights ideas to describe where authority sits. The study connects governance with shadow IT in a setting students already know.
10. Post-implementation review practice: how many public bodies publish one, and what do those that do actually measure? Search the websites of 30 public bodies for published reviews and code what each measures, such as cost, benefits, user satisfaction or security. This is a suitable first project because it needs no interviews and gives a clear count.
ERP and enterprise systems decisions
11. SAP ECC mainstream maintenance ending on 31 December 2027: how mid-sized manufacturers choose between S/4HANA conversion, extended maintenance to 2030 and third-party support. SAP’s own announcements give the end of mainstream maintenance in 2027 and an extended option to 2030. Interview ERP leads in three to five firms and use real options reasoning to compare their choices. Check SAP’s current maintenance notices, because dates and offers can change.
12. Brownfield or greenfield: customisation retained and abandoned in S/4HANA programmes at three organisations. Compare how much custom code each organisation kept and why, using project documents and interviews. Two cases are enough for an undergraduate project if the contrast is clear.
13. Clean-core governance: who approves extensions to a cloud ERP, and how approval rules shape the number of workarounds. “Clean core” is the vendor-promoted idea of keeping the standard system untouched and building extensions alongside it. Treat that as the practice you test rather than a settled benefit. A single case with access to the extension request log would work well.
14. Workarounds as data: classifying the spreadsheets that shadow an ERP in one finance team. List the spreadsheets, then classify each by purpose, such as reporting, correction or control. Task-technology fit gives you a theory for explaining why they exist. The method is simple enough for an undergraduate project.
15. Super-user networks after go-live: do departments with active super-users log fewer helpdesk tickets in the first six months? Normalise tickets per user, because department size would otherwise distort the comparison. The design is quasi-experimental, so describe it as an association and discuss confounders honestly.
16. Master data errors and reporting variances: tracing 20 sampled discrepancies back to their source in one organisation’s ERP. Pick discrepancies from management reports and trace each back through the data chain. Report the sources by category, such as entry error, interface failure or definition difference.
17. Enterprise architecture repositories in higher education: are they consulted when investment decisions are made? Survey architects and IT leaders, then check a sample of investment papers for references to the repository. The gap between stated and actual use is the finding.
18. Customer master data after an acquisition: building a single customer view across two CRM and billing systems, and the rules that decide the surviving record. Design science fits a Master’s student with some data skills. Document the matching rules, test them on anonymised samples and report false matches and missed matches.
19. Robotic process automation in finance shared services: residual manual steps and exception handling six months after deployment. Observe one automated process and count the steps that still need a person. Compare the result with the original business case.
Legacy systems, digital government and public services
Government and NHS topics are UK-specific, but the same questions can be asked about another country’s public sector, and a comparison often improves the project.
20. How do organisations define a legacy system? Comparing the definitions behind the 28% central government estimate in the State of Digital Government review. The January 2025 review estimated that 28% of central government systems were legacy in 2024, up from 26% in 2023, and noted that most public bodies lack comprehensive registers. Compare definitions across published guidance and add a short survey of IT asset managers if you can reach them.
21. Unsupported systems in NHS trust risk registers: how trusts word, score and escalate legacy IT risk. The same review found legacy levels in NHS trusts ranging widely, from about 10% to 60 or 70%. Freedom of Information requests for risk-register entries give you comparable text to code. Check which entries each trust is allowed to release.
22. Legacy IT risk in principal risk statements: how large UK listed companies describe ageing systems in their annual reports. Content analysis of 50 reports is a Master’s scale. Fifteen reports with a clear coding sheet suit an undergraduate project.
23. Wrapping mainframe functions in APIs instead of replacing them: what organisations gain and what risk remains. The review discusses how legacy systems limit data sharing. A case study or a design science project could test an API wrapper on a small, safe function and document what the old system still controls.
24. Services without a digital pathway: which service characteristics go with having no digital route, given that 47% of central government and 45% of NHS services lacked one in the review? Build your own coded sample of about 60 public services and record features such as identity checks, payments and evidence uploads. Describe patterns rather than causes, because you will not control for everything.
25. Departmental migration to GOV.UK One Login: barriers named in public documents and parliamentary evidence. Keep to one department to stop the scope growing. Document analysis, coded by barrier type, works without interviews.
26. Digital right-to-work checks: how employer HR and IT teams adapted to share-code verification, and what a mandatory digital check by 2029 may require. Digital identity checks for right to work began in 2022. In January 2026 the government made the planned digital ID optional but said it remained committed to mandatory digital right-to-work checks. Interview HR and IT staff in three employers and check the Home Office position again before you submit.
27. Companies House identity verification since 18 November 2025: how company secretarial software providers and corporate service providers changed their workflows. Identity verification for directors and persons with significant control became mandatory on that date, with a 12-month phase for existing roles. Process-map two or three providers and compare it with the official guidance, which is the authority if details have changed.
28. Making Tax Digital for Income Tax: software adoption by sole traders and landlords above the £50,000 start threshold, and the later £30,000 and £20,000 waves. The government collection sets the first wave for 6 April 2026, with lower thresholds following in 2027 and 2028. A UTAUT2-based survey of first-wave traders is practical. Define qualifying income exactly as HMRC does, or your groups will not match the rule.
29. Mandatory e-invoicing from April 2029: readiness of small suppliers and the choice of a Peppol access point. The government announced the April 2029 date at Budget 2025 and confirmed Peppol as the core network in June 2026, with a fuller roadmap expected at Budget 2026. Treat the mandate as announced policy until legislation appears. Interviews with accounting software providers and small suppliers would show who is preparing and who is waiting.
30. The NHS Single Patient Record: how it could build on shared care records, electronic patient records and the Federated Data Platform, as NHS England describes it. NHS England’s programme description says the record will build on existing systems rather than replace them. Policy and document analysis avoids NHS ethics approval, which stakeholder interviews would require. Stay neutral on contested points such as supplier involvement, and describe positions rather than taking sides.
31. Published governance of the Federated Data Platform: what check-and-challenge group minutes say about access controls, opt-outs and trust adoption. NHS England publishes minutes from this group, so you can code them over time. Note what the minutes leave out as well as what they record.
32. Interoperability standards in health IT tenders: how NHS procurement documents specify FHIR and other standards. Collect 20 tender documents from public notices and code how firmly each requires a standard. Compare requirements with the system functions being bought.
33. Digital Economy Act information-sharing powers extended in 2026 to support businesses and charities: what safeguards do published data-sharing agreements specify? Regulations commenced in February 2026 extended these powers. Check first which agreements are public. If few are, redesign the project as a comparison of the statutory safeguards with agreements from earlier schemes.
IT governance, strategy and alignment
Governance questions that lean towards boards and company law may also fit the corporate governance dissertation topics list.
34. COBIT 2019 and ISO/IEC 38500 as lenses for board oversight of IT in one university: where the two frameworks disagree in practice. These are practice frameworks, not theories, so state that distinction early. Apply both to a set of board papers and record which questions each framework would ask but the board did not.
35. Board technology committees in large UK listed companies: which firms disclose one, and what its terms of reference cover. Annual reports are public and the data is easy to collect. Code the terms of reference for oversight of cyber, data, AI and major projects.
36. CIO reporting lines in higher education: does reporting to the vice-chancellor’s executive change how digital strategy documents are written? Compare the reporting lines in public organisation charts with the content of 20 published strategies. The study shows whether proximity to power shows up in strategy language.
37. Strategic alignment in practice: applying Henderson and Venkatraman’s model to IT investment appraisals in one local authority. Code a sample of appraisals for links between IT proposals and corporate priorities. A single case with documents is enough.
38. IT capability or IT spending: do capability measures explain performance better than spend in a survey of mid-sized firms (PLS-SEM)? This tests an idea from the resource-based view. You need enough respondents, so use the sample size calculator early, and plan for common method bias. It suits a Master’s or PhD project.
39. Shadow IT in business units: detecting unsanctioned software through expense data and the consequences for IT governance. Use anonymised expense or card data from one organisation and classify the tools found. Pair the results with interviews on why teams bought outside the approved list.
40. Exit and termination terms in published public-sector IT contracts: content analysis of contracts on Contracts Finder. Many published contracts are redacted, so build your sample from those that include exit schedules. Code the clauses by notice period, data return and assistance.
41. What does “digital” mean in local authority digital strategies? Text analysis of 40 published strategies. Use topic modelling for a Master’s project. For an undergraduate project, hand-code 10 strategies for the services they promise to change.
42. Decision rights for IT and data in a federated university: mapping who decides, using Weill and Ross’s governance archetypes. Interview staff across faculties and the central service, then map each major decision to an archetype. The finding is often a mismatch between the policy and the practice.
43. IT investment in family-owned firms: how overlapping ownership and management shapes system decisions. Stewardship and agency theory give opposite predictions, which makes the comparison useful. Two or three case firms with interviews would be a realistic Master’s design.
Cyber governance and organisational resilience
These topics approach security as a management problem. Technical testing and attack detection projects belong with the cybersecurity dissertation topics, and legal analysis fits the cyber law dissertation topics. The NCSC Annual Review 2025 reported 204 nationally significant incidents between September 2024 and August 2025, up from 89 the year before, which explains the policy attention.
44. Board responsibility for cyber security: why only 31% of UK businesses formally assign it in the 2025/26 Cyber Security Breaches Survey, and what separates the firms that do. The survey published its findings on 30 April 2026. Secondary analysis of the published tables plus a few interviews would work. Remember that the survey covers only breaches organisations identified and were willing to report.
45. Cyber insurance and reported controls: do firms that hold insurance report different security practices in the survey tables? The survey found that just under half of businesses reported some cyber insurance. Treat any difference as an association and discuss moral hazard and selection as competing explanations.
46. Two-stage incident reporting in the Cyber Security and Resilience Bill (24 hours, then 72 hours): redesigning incident response in a managed service provider. Law firm commentary describes an initial notification within 24 hours and a fuller report within 72 hours. Design a workflow with decision points, test it in a walkthrough with practitioners and record the legal text version you used. Parliament’s Bill page shows the current stage, and the details may change in the Lords.
47. One decision flow for three duties: mapping incident notification under the Bill, the UK GDPR 72-hour personal data breach rule and a sector regime for a mid-sized organisation. The artefact is a decision tool, so design science fits. Test it on three invented but realistic incident scenarios and ask a compliance practitioner to review the outputs.
48. Supplier concentration in the 2025 retail and manufacturing incidents: what trading statements, regulatory announcements and committee correspondence reveal about supplier governance. Parliament’s Business and Trade Committee wrote to Tata Consultancy Services about attacks on Jaguar Land Rover, Marks and Spencer and the Co-op. Use only public documents and avoid claiming causes that no source states.
49. Reporting the cost of a cyber incident: comparing how Marks and Spencer and Jaguar Land Rover disclosed direct costs, insurance recoveries and lost sales. Stock-exchange announcements and results statements are the evidence. Build a comparison table and discuss what each disclosure would let an investor judge.
50. Government loan guarantees after cyber incidents: moral hazard and resilience investment in the £1.5 billion guarantee for Jaguar Land Rover. The government announced the guarantee in September 2025. Some security specialists warned it could encourage attackers, while the government framed it as protecting the supply chain. A policy analysis for a Master’s or PhD project should set out both arguments and the evidence each uses.
51. The Govern function in NIST CSF 2.0 against ISO/IEC 27001:2022: a gap assessment tool tested with a small organisation. NIST released version 2.0 in February 2024 and added Govern as a sixth function. Map its outcomes to the ISO controls and clauses and test the tool with one organisation. Report what the tool missed.
52. After the 31 October 2025 deadline for ISO/IEC 27001:2013 certificates: how customer procurement teams treat suppliers whose certificates lapsed or are mid-transition. Interview procurement and supplier assurance staff and review a few supplier questionnaires if you can obtain them. The study shows what certification means in practice for buyers.
53. Cyber Essentials in tenders: how buyers weigh certification and what suppliers say it costs in time. Survey small suppliers and interview two or three buyers. Keep claims about security benefit separate from claims about winning contracts.
54. Windows 10 end of support on 14 October 2025: how organisations prioritised endpoint upgrades against paid security updates, and what Cyber Essentials expected afterwards. The scheme’s guidance said Windows 10 users had to be enrolled in Microsoft’s Extended Security Updates programme after the date to stay compliant. Interview IT managers about upgrade sequencing and check the current scheme requirements before you write.
55. Coding publicly reported UK incidents with the NCSC and law enforcement categorisation model. The model places the upper three categories in the “nationally significant” group. Build a coding sheet from public descriptions and be clear that confidential incident data is not available to you.
56. Security policy compliance among remote workers: testing protection motivation theory with a staff survey. Measure threat appraisal, coping appraisal and reported compliance. A valid scale from earlier studies saves time and improves credibility.
57. Phishing simulation results as management data: what a case organisation measures beyond click rates. Look at reporting rates, time to report and repeat clickers. Anonymise heavily, because staff-level results are sensitive.
Data governance, privacy law and cross-border data
Data rules change what an organisation can store, share and automate, so they make strong management topics. Statutes and enforcement notices are public, which gives you primary evidence without needing insider access.
58. How did UK organisations change their data protection governance after the Data (Use and Access) Act 2025 changes to UK GDPR came into force in early 2026? Compare privacy notices, record-keeping and complaints handling before and after. Use the ICO guidance and the Act itself, and check the commencement regulations for the exact dates that apply to each provision.
59. Recognised legitimate interests under the Data (Use and Access) Act 2025: whether compliance teams in a sector are using the new lawful basis and why. Interview data protection officers in one sector. Ask what they changed in their lawful basis records, and what they decided to leave alone.
60. Data subject access requests as an operations problem: volumes, redaction effort and tooling in one local authority, using published performance data and Freedom of Information responses. Ask for request counts, response times and the systems used to search records. Report the limits of what a public body is willing to release.
61. ICO monetary penalty notices as case material: what the published notices say about weaknesses in management controls rather than technical faults. Code the notices for governance themes such as supplier oversight, access control and incident response. Use only published notices and state the date range you coded.
62. The Capita data breach penalty from the ICO: what the notice reveals about supplier oversight when an outsourcer holds pension and public-sector data. Read the full notice before you write anything. Build a case around what the controller and the processor each failed to manage, and keep your conclusions tied to the text.
63. Data protection impact assessments in practice: how project teams decide whether a new system needs one, and who signs it off. Collect templates from willing organisations and interview two or three project managers. A small, well-described comparison beats a large, shallow survey.
64. Records of processing as a living asset: why spreadsheets drift out of date and what a case organisation does to keep them current. Observe or interview the team that maintains the record. Link your findings to the accountability principle in UK GDPR.
65. EU Data Act switching rights for cloud and data processing services, applicable from 12 September 2025: how suppliers have rewritten contract terms, using published standard terms. Compare the public terms of three providers before and after the date. Treat this as document analysis and say clearly that you cannot see negotiated contracts.
66. Standard contractual clauses and the UK International Data Transfer Agreement: what organisations document when they move personal data out of the UK. Review the ICO transfer risk assessment materials and interview one privacy lead. If the EU and US transfer arrangements have changed since you started, record the date you checked.
67. Data quality ownership: who is accountable when the same customer record lives in four systems, tested through a single-organisation case study. Map the systems, then interview the owners of each. Use a simple accuracy and duplication audit on a sample extract, with permission and with identifiers removed.
68. Open banking and smart data schemes under the Data (Use and Access) Act 2025: organisational readiness among small financial firms or energy suppliers. Pick one scheme and one sector. Interview compliance and product staff, and keep to what the regulator has published so far, as rules are still being made.
69. Freedom of Information requests as a data source: what a sample of public bodies disclose about IT contract values and supplier concentration. Send the same short request to a set of bodies and record response quality and delay. Note that the process itself is part of your findings.
70. Privacy by design in public-sector procurement: whether tenders published on Find a Tender ask suppliers for data protection evidence under the Procurement Act 2023. Sample notices and tender documents and code the data protection requirements. Check which notices fall under the new regime before you build your sample.
Cloud, sourcing and platform dependence
Sourcing decisions tie an organisation to suppliers for years. Regulators, auditors and parliamentary committees publish a lot about them, which suits desk-based and interview-based projects.
71. Cloud egress fees and licensing as lock-in: what the CMA cloud services market investigation found and how an IT manager might respond, using the published final decision. Read the final decision and its remedies. Interview IT managers about exit planning and test whether the concerns in the report match what they describe. Check the CMA case page for any later steps.
72. Exit plans for cloud contracts: do they exist, and who tests them, in mid-sized organisations? Survey or interview IT and procurement leads. Compare answers against the exit provisions in DORA, ISO/IEC 27001 supplier controls or sector guidance that applies to your respondents.
73. The July 2024 CrowdStrike update failure as a change management case: vendor update controls, staged rollouts and recovery plans in organisations that were affected. Use public post-incident reviews and vendor statements, and interview one or two IT staff if you can. Separate what the vendor controlled from what customers could have controlled.
74. Digital Operational Resilience Act (DORA) register of information: how EU and UK-linked financial firms manage ICT third-party data, and what it costs them in staff time. DORA has applied since 17 January 2025. Interview risk and vendor managers, and use the regulation text and the supervisory authority templates. Keep it distinct from DevOps DORA metrics.
75. The UK critical third parties regime for financial services: how banks expect to change vendor monitoring if a cloud provider is designated. Use the Bank of England, PRA and FCA papers. Check the latest designation position at the time you write, as it may have moved.
76. Cloud cost management and FinOps practice: how finance and IT teams share responsibility for variable spend. Compare the FinOps Foundation framework with what two organisations actually do. Measure outcomes with cost reports they are willing to share in summary form.
77. Why some organisations move workloads back from public cloud: a multiple-case study of repatriation decisions. Use published conference talks, vendor case studies and interviews. Watch for survivor bias, because firms that stay in the cloud rarely write about it.
78. Software as a service sprawl: how a university or NHS trust finds and governs applications bought outside central IT. Use procurement records, single sign-on logs if available, and interviews. Present this as a governance problem and keep security detail high level.
79. Low-code platforms in local government: who builds, who supports, and what happens when the builder leaves. Interview citizen developers and the central team. A simple capability and risk matrix helps you compare cases.
80. Open source in the public sector: how UK and EU bodies justify using or avoiding open source software in published policy and procurement notices. Collect strategy documents and tender text, then apply content analysis. Keep a clear list of the documents you included and why.
AI in organisations: governance, adoption and accountability
Many students pick AI topics, so the way to stand out is to choose a narrow organisational question rather than a technology review. Keep your claims to what a case organisation or a public document supports.
81. How have organisations structured AI governance against ISO/IEC 42001 and the NIST AI Risk Management Framework, and where do the two disagree in practice? Compare the published frameworks, then check them against interviews with governance or risk staff. Do not claim an organisation is certified unless it says so publicly.
82. AI literacy duties under Article 4 of the EU AI Act: what training UK firms with EU customers have introduced for staff, and how they decide who needs it. Article 4 has applied since 2 February 2025. Interview learning and compliance leads. Check the current text and any official guidance, because implementation timetables for other parts of the Act have been under discussion.
83. EU AI Act high-risk obligations and the proposed delay: how a software vendor plans its roadmap when the dates are uncertain. Use the Regulation, Commission proposals and one vendor case. Say exactly which version of the timetable you used and the date you checked it.
84. The Algorithmic Transparency Recording Standard in central government: what departments disclose, and what is left out. Code a sample of published records against the standard’s fields. Report patterns in completeness, not opinions about whether a tool is good.
85. The UK AI Playbook for government and frontline adoption: whether a civil service team’s practice matches what the playbook asks of them. Interview staff in one team or analyse published case studies. Be careful with confidentiality, because internal evaluations are often unavailable.
86. Shadow AI: how staff use public generative tools for work, and what a policy changes, measured with an anonymous survey in one organisation. Ask about tool use, data types entered and awareness of policy. Use a validated adoption scale as a base and keep questions neutral. Have your supervisor approve the ethics process first.
87. Microsoft 365 Copilot or a similar assistant: a pilot evaluation in one team using task-technology fit. Define tasks, collect time and quality measures before and after, and add short interviews. State clearly that results come from one team and cannot be generalised.
88. Who is accountable when an automated decision goes wrong? Role clarity in a case organisation using the RACI method. Map the decision path from data to outcome and ask each role who they think owns the error. Compare the answers with the written policy.
89. Generative AI in internal audit and compliance teams: where professionals draw the line between assistance and judgement. Interview auditors or compliance officers and use professional body guidance. The theory of professional jurisdiction or dual-process models can structure your analysis.
90. Explainable AI and trust among caseworkers: what staff need to be told before they rely on a risk score. Use vignettes in a short experiment or a set of interviews. A small, careful design is better than an underpowered survey.
91. Customer service chatbots and handover to humans: what complaint data from an ombudsman or regulator says about failures in automated front doors. Use published complaint decisions and regulator reports. Code them for the point where automation stopped helping, and avoid naming individual customers.
Users, behaviour and digital inclusion
Many information systems fail because people do not use them as designed, so behaviour is a legitimate management question. Pick a defined group of users and a defined system.
92. Why do clinicians work around electronic patient record systems? A technology-in-practice analysis in one ward or practice. Use observation notes or interviews and apply Orlikowski’s technology-in-practice lens. Ethics and NHS research approval may be needed, so plan time for it.
93. UTAUT2 habit and hedonic motivation among students using a learning platform: which constructs actually predict continued use? Use a validated questionnaire and PLS-SEM or regression. Keep the sample to one institution and report reliability and validity checks clearly.
94. Technostress in hybrid teams: how video meeting load and constant notifications relate to reported exhaustion among office workers. Use a published technostress scale. Control for job role and working pattern. Treat results as associations, not causes.
95. The NHS App and digital exclusion: which patient groups report barriers, using published survey data and a short local survey. Draw on NHS England and Healthwatch reports, then add a small community sample. Handle health information with care and keep it non-clinical.
96. Accessibility of local authority online services against WCAG 2.2 AA and the Public Sector Bodies Accessibility Regulations 2018: an audit of a sample of council websites. Use automated checkers plus manual checks on a task flow. Explain the limits of automated testing and publish no personal data.
97. GOV.UK One Login and user trust: what users say about repeat identity checks across services. Use public user research, forum posts as secondary data with an ethics note, and interviews if possible. Check the current state of the identity programme before you write.
98. Digital skills gaps in small firms: what the ONS Business Insights and Conditions Survey and Lloyds Consumer Digital Index suggest about who falls behind, and what managers say they need. Combine a secondary data analysis with a small interview set. Avoid broad claims about all small firms.
99. Older adults and online public services: how family members act as intermediaries, and what that means for system design and consent. Interview intermediaries and users. Anonymise carefully and keep the focus on service design.
100. Neurodiversity and enterprise software: how interface and notification settings shape the daily work of neurodivergent employees. Invite voluntary participation and keep disclosure optional. Use a participatory design approach and report only what participants approve.
101. Gig platform workers and algorithmic management: how rating and allocation rules shape control, using the Uber v Aslam employment status judgment as a starting context. Use court documents, platform terms and worker interviews or public forums. State the legal position as of your reading date and avoid giving legal advice.
102. Resistance, workaround or adoption? A case study of a finance system change using escalation of commitment and sensemaking. Interview project sponsors and users at different stages. Show how each group describes the same decision.
Green IT, sustainability and measurement
Sustainability reporting is moving into IT teams, so measurement and accountability questions are easy to defend. Use published methods rather than inventing your own carbon factors.
103. Software Carbon Intensity (ISO/IEC 21031:2024): can a team calculate it for one application, and what do they need to know to do so? Apply the specification to a small system you can access, document your assumptions, and show how results change if assumptions change.
104. Hardware refresh cycles in universities: what is lost or gained by extending laptop life from four years to six, using procurement data and interviews. Use life-cycle assessment data from manufacturers and public sector guidance. Be clear about boundaries, such as whether you include manufacturing emissions.
105. Data centre energy reporting under the EU Energy Efficiency Directive: how operators describe efficiency and water use, using published reports. Check which obligations apply and from when. Compare disclosures across a small set of operators, and avoid inferring performance from marketing claims.
106. Greening government ICT: how departments report IT emissions in annual reports, and whether the figures can be compared. Read annual reports and sustainability sections for several years. Create a coding table for scopes and methods, then report what cannot be compared.
107. Scope 3 emissions from cloud services: how a UK firm allocates supplier-reported figures into its own reporting under the GHG Protocol. Interview a sustainability reporting lead. Compare the allocation methods offered by cloud suppliers and report their differences.
108. E-waste handling in small organisations: what happens to devices when no one owns the policy? Survey or interview office managers and compare answers with WEEE guidance. Include a short device audit if possible.
109. Measuring the benefits of IT investment beyond cost: applying DeLone and McLean to one sustainability reporting system. Collect system use, user satisfaction and net benefits data. Test whether the model’s links hold for a small organisation and explain why they might not.
Four worked examples: from topic to aim and objectives
These show how a topic becomes a plan. Use them as models and adapt wording to your supervisor’s preferred style.
Example 1: supplier oversight after a data breach
Topic: The Capita data breach penalty from the ICO and supplier oversight (topic 62). Aim: to explain which management controls over a processor the ICO treated as inadequate and how those controls compare with published guidance. Objectives: (1) code the penalty notice for control failures; (2) compare them with ICO guidance on controller and processor duties; (3) interview two data protection practitioners about how their own supplier checks differ.
Example 2: cloud exit planning
Topic: Exit plans for cloud contracts in mid-sized organisations (topic 72). Aim: to assess how far exit planning is documented and tested. Objectives: (1) design a short survey on exit clauses and testing; (2) compare responses against DORA and ISO/IEC 27001 supplier expectations; (3) run three follow-up interviews to explain gaps.
Example 3: AI governance in practice
Topic: AI governance against ISO/IEC 42001 and the NIST AI RMF (topic 81). Aim: to compare the framework expectations with practice in two organisations. Objectives: (1) build a comparison table of the two frameworks; (2) interview governance staff; (3) identify where practice follows one framework but not the other.
Example 4: accessibility audit
Topic: Accessibility of local authority online services against WCAG 2.2 AA (topic 96). Aim: to measure conformance on a key task across a sample of councils. Objectives: (1) select 20 councils and one common task, such as reporting a missed bin collection; (2) test with automated tools and manual checks; (3) summarise common failures and compare large and small councils.
How to turn an information systems idea into a researchable title
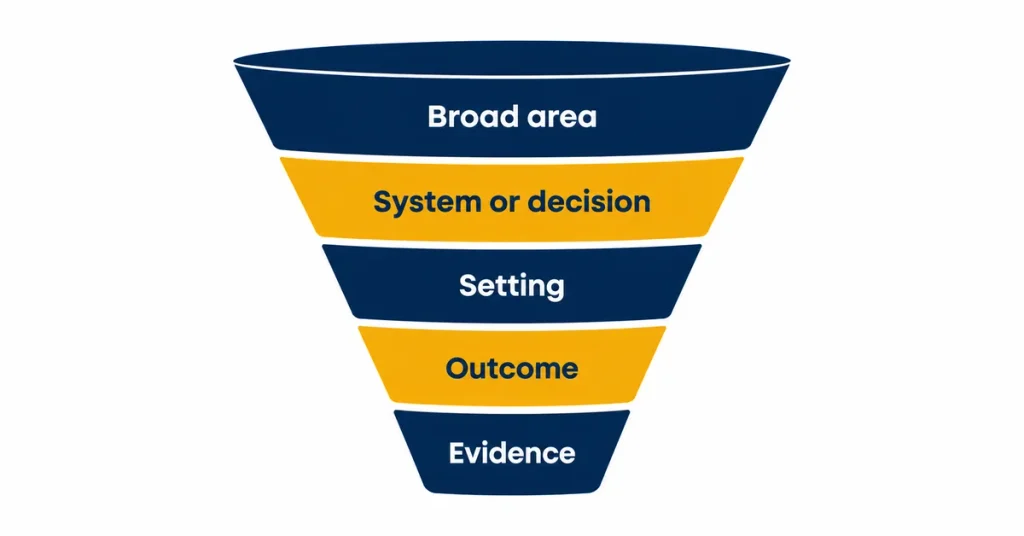
Start with a broad area, then narrow it by system, setting, time and evidence. For example, “cloud adoption” becomes “exit planning in cloud contracts” and then “exit plans in mid-sized UK organisations tested against DORA and ISO/IEC 27001”. Each step removes ambiguity and makes the data question clearer.
- Name the system or decision. ERP replacement, a supplier contract, an AI tool or a security programme.
- Name the setting. One organisation, one sector or one regulator.
- Name the outcome. Adoption, cost, compliance, resilience or user trust.
- Name the evidence. Interviews, a survey, public documents or open data.
- Test access early. If you cannot get the evidence in two weeks, change the topic.
If you need help turning an idea into a question, the dissertation topic finder and the guide to writing a research question take you through it step by step.
Which methods suit information systems management dissertations?
- Interpretive case study suits adoption, governance and workaround questions. Benbasat, Goldstein and Mead (1987) and Klein and Myers (1999) are standard references.
- Survey with PLS-SEM or regression suits technology acceptance and compliance behaviour. Use validated scales and report reliability.
- Design science suits a small artefact, such as a dashboard or checklist, evaluated with users. Hevner et al. (2004) and Peffers et al. (2007) set out the steps.
- Document and content analysis suits regulation, penalty notices, tenders and annual reports.
- Secondary data analysis suits ONS, DSIT and Eurostat data where you have no access to an organisation.
The guide to choosing a research methodology explains how to match method to question, and the statistical test selector helps once you have survey data.
Theories and frameworks: which is which?
A theory explains why something happens. A framework or standard tells practitioners what to do. Mixing the two is a common marking issue.
- Theories: TAM (Davis, 1989), UTAUT (Venkatesh et al., 2003), DeLone and McLean (2003), technology-organisation-environment, task-technology fit (Goodhue and Thompson, 1995), the resource-based view, strategic alignment (Henderson and Venkatraman, 1993), protection motivation theory.
- Practice frameworks and standards: COBIT 2019, ITIL 4, ISO/IEC 27001:2022, ISO/IEC 38500, ISO/IEC 42001, NIST CSF 2.0.
Use a theory to explain results and a framework to judge practice, and say which role each one plays in your study.
Where can you find UK and international data for these topics?
- Cyber Security Breaches Survey for organisational security practice.
- ONS Business Insights and Conditions Survey for technology and AI use in UK businesses.
- Information Commissioner’s Office for guidance, penalty notices and data security incident trends.
- National Audit Office for reports on government IT and digital programmes.
- Contracts Finder and Find a Tender for public contract notices.
- CMA cloud services market investigation for the evidence and decisions on cloud competition.
- EU AI Act text, EU Data Act text and DORA text for the legal wording.
- NIST AI Risk Management Framework and ISO/IEC 42001 for AI governance.
- Algorithmic Transparency Recording Standard hub for public-sector AI records.
- Public Sector Bodies Accessibility Regulations 2018 and WCAG 2.2 for accessibility audits.
- Software Carbon Intensity specification for green software measurement.
Always note the date you accessed each source, because guidance and legislation are updated.
What are the most common mistakes in information systems management dissertations?
- Choosing a technology instead of a management question. “Blockchain” is a topic area; “supplier governance in a blockchain pilot” is a question.
- Treating a framework as a theory. COBIT does not explain behaviour; it describes controls.
- Claiming access you do not have. Confirm interviewees or data before you write the proposal.
- Using outdated rules. Check the current status of Bills, regulations and standards and state the date.
- Generalising from one case. Say what a single organisation can and cannot tell you.
- Skipping ethics. Staff surveys and interviews usually need approval, and security topics need extra care.
Information systems management dissertation topics FAQs
What makes a good information systems management dissertation topic?
A good topic names a system, a setting, an outcome and a source of evidence. If you can describe what you will collect and from whom in one sentence, it is probably narrow enough.
Is information systems management the same as management information systems?
They overlap, and universities use the names differently. In most programmes, management information systems focuses on how information systems support management decisions, while information systems management focuses on governing, delivering and running those systems. Check your module handbook for your department’s wording.
Do I need technical skills for these topics?
Not for most of them. Governance, adoption, policy and user behaviour topics rely on interviews, surveys and documents. Technical topics, such as measuring software carbon intensity, need some access to the system but not advanced coding.
Can I use a public case study instead of fieldwork?
Often yes. Penalty notices, audit reports, inquiry volumes and tender documents are valid sources. Say why you chose them, set a clear coding method and explain what the material cannot show.
How many topics should I shortlist before choosing?
Shortlist three. Test data access for each, read two or three recent papers on them, and pick the one where evidence is easiest to reach. The guide to choosing research topics can help you compare your options.
What should you do next with your information systems management topic?
Pick one title, rewrite it as a research question, and draft an aim and two or three objectives. The research aims and objectives generator can give you a starting structure, and the guide to aims, objectives and research questions explains how they fit together. All the topics above are free to use and adapt.
For related ideas, see our business information technology dissertation topics, artificial intelligence dissertation topics, business intelligence dissertation topics and change management dissertation topics.
If you want a specialist to check your proposal or develop the full project, you can look at our IT dissertation help or research proposal writing service. Free revisions and a free plagiarism report are included with orders.